Non-human identities
Secure and govern non-human identities (NHI) at scale
Find every NHI across cloud, SaaS and on-prem. Give each an accountable owner, see what it can reach, and disable dormant ones.
Non-human identities outlive their purpose
Heading
No one owns them
Creators move on, and their service accounts and keys stay behind.
Dormant but privileged
Idle accounts keep full privileges long after their last use.
Credentials never rotate
Keys and tokens age for years without anyone noticing.
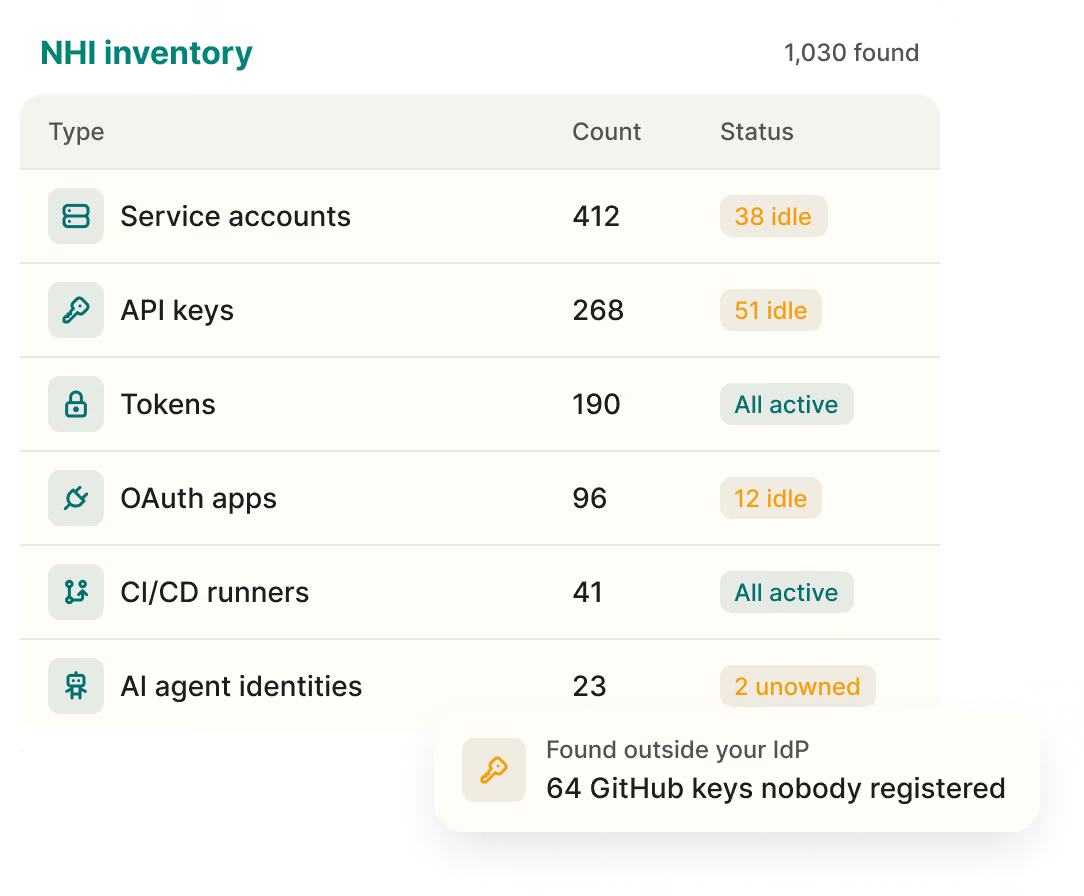
Every service account, key, and token

Every NHI, wherever it lives
Discover NHIs across IdPs, SaaS, cloud, code, and custom apps.

One graph for every identity
Mapped alongside human identities and AI agents, with activity on each.
An accountable owner for every NHI

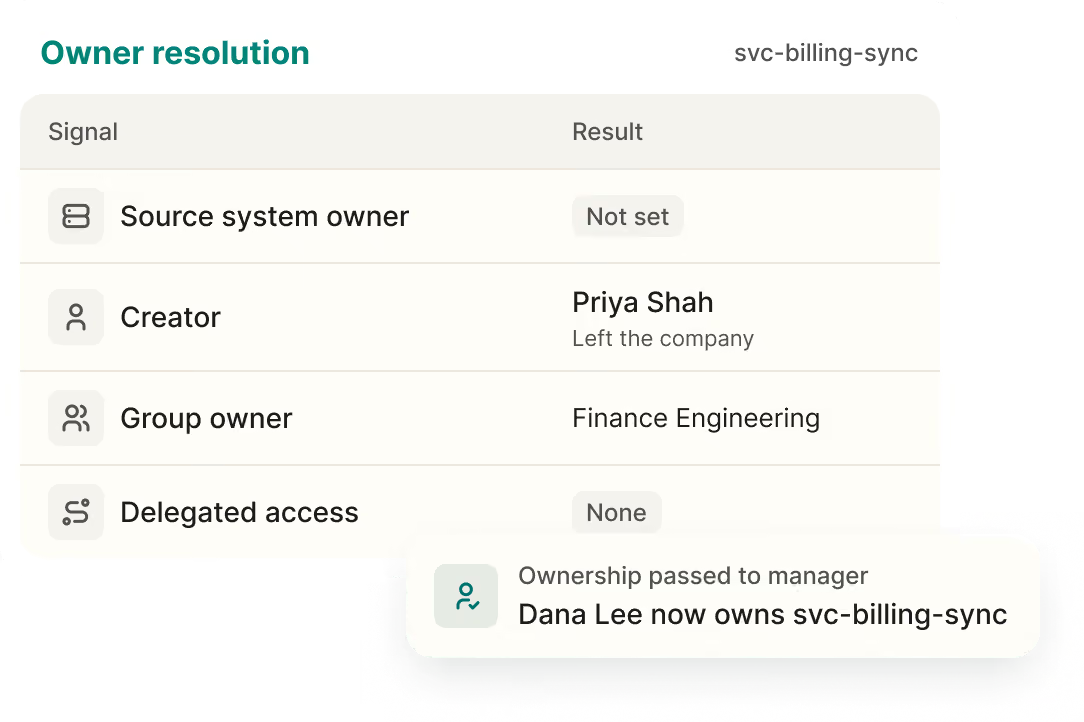
Owners from real signals
Oleria finds each owner from the source system, the creator, group owners, and delegated access.

Ownership that follows people
If an owner leaves, ownership passes to their manager.
Know what each NHI can reach
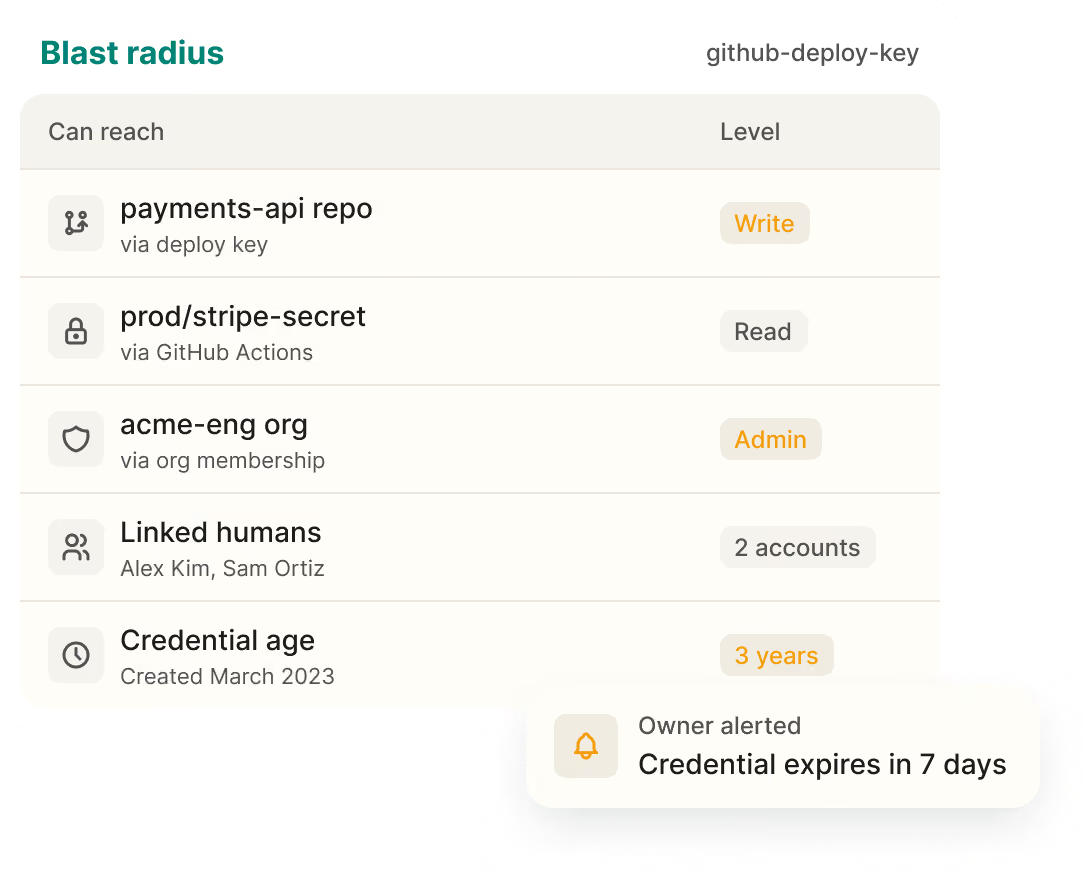
Access paths and privilege
See every path an NHI can use, and how much it can do.

Linked human accounts
See which people each NHI is tied to.

Credential age
Owners are alerted before credentials expire.
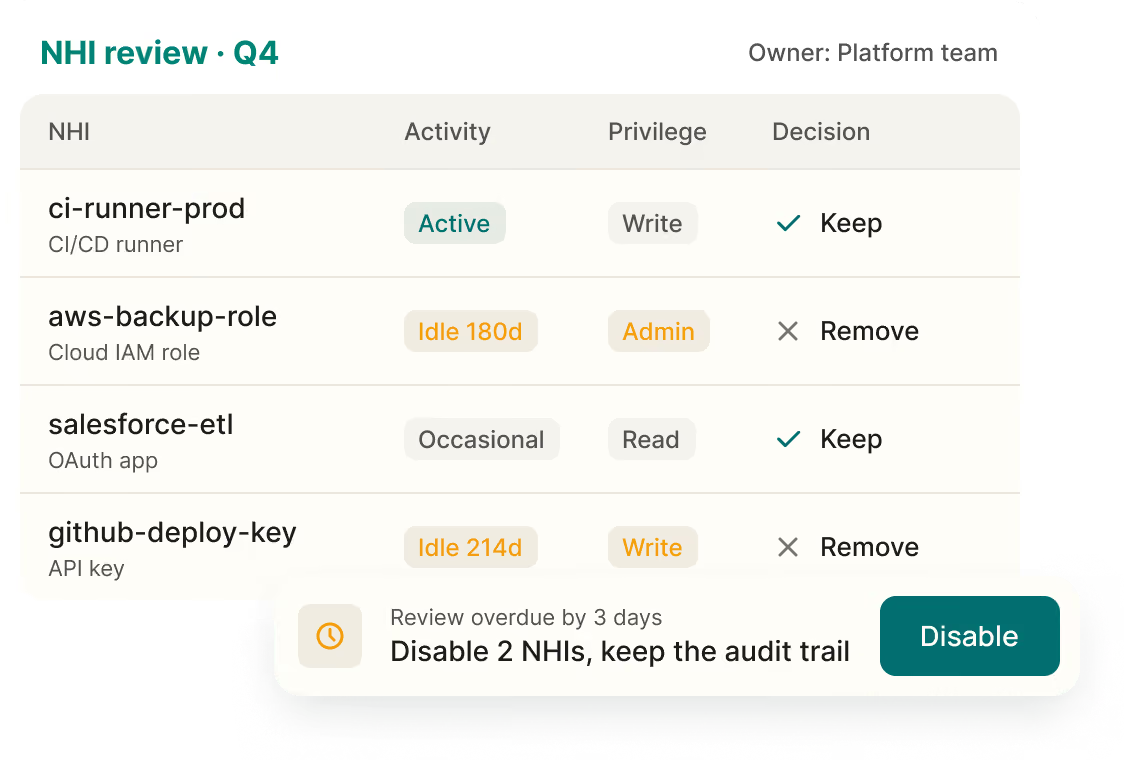
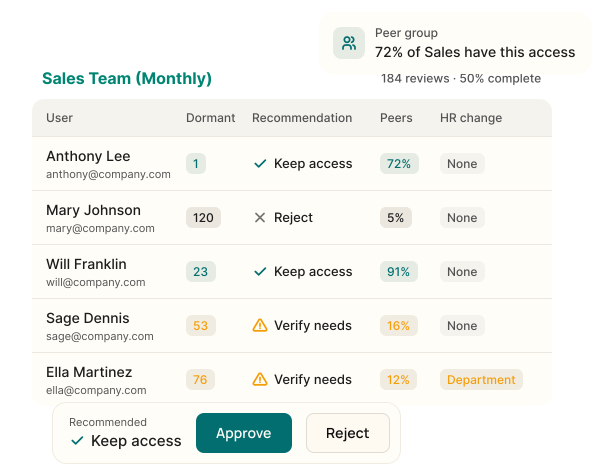
Review NHIs like human identities

Activity in view
See whether each NHI is active, idle, or used only occasionally.

Overdue reviews enforced
If a review goes overdue, Oleria can disable the NHI.

Full audit trail
Every decision and action is kept for auditors.
Real customers. Real results.
Security teams use Oleria to clean up excess access, get through audits faster, and bring AI agents under control

Oleria is one of those things that once you see it and get it, it’s hard to imagine doing what you’ve been doing without it.
Being able to assess the current state and optimize around least privilege provides the ROI in itself.And the ability to understand what my engineers need will help us provide least- privilege access
Oleria gives us unparalleled visibility into identity access and usage, saving time and strengthening our compliance posture.
Beyond discovery: ownership, reviews, and fixes


Learn more about NHI governance
What is non-human identity (NHI) governance?
Non-human identity (NHI) governance controls the access held by service accounts, API keys, tokens, bots, and other automated identities. Oleria discovers every NHI, assigns an owner, tracks activity and credential age, and reviews access so nothing keeps privileges after its purpose ends.
What NHI types does Oleria discover?
Service accounts, API keys, tokens, OAuth apps, bots, CI/CD runners, AI agent identities, shared mailboxes, cloud IAM roles, managed identities, and certificates.
Which systems does Oleria discover NHIs in?
No. Oleria AI is the intelligence built into the Trustfusion platform you already know. The naming gives a clear identity to a capability that spans every workflow on the platform, governance, risk, investigations, access, and the MCP endpoint rather than presenting AI as a separate SKU or a bolt-on feature.
Oleria discovers NHIs across identity providers such as Okta and Entra ID, cloud platforms including AWS, Azure, and Google Cloud, code platforms such as GitHub, SaaS apps like Salesforce and ServiceNow, and custom apps.
How does Oleria assign NHI owners?
Oleria uses the strongest signal available: the owner recorded in the source system, the creator, a group or role owner, delegated access or audit logs If none is found, the NHI goes to a reviewer. If an owner leaves, their manager takes over.
Does Oleria integrate with secrets managers?
Yes. Oleria surfaces credential risk and works with secrets managers such as HashiCorp Vault and AWS Secrets Manager to coordinate rotation.
Learn more about non-human identity governance
Guides and customer stories on finding, owning, and governing service accounts, API keys, and tokens.