Posture Management
Identity security posture (ISPM), from finding to fix
Find MFA gaps, risky passwords, misconfigured apps, and excess access across every identity, ranked by risk and fixed in one place.
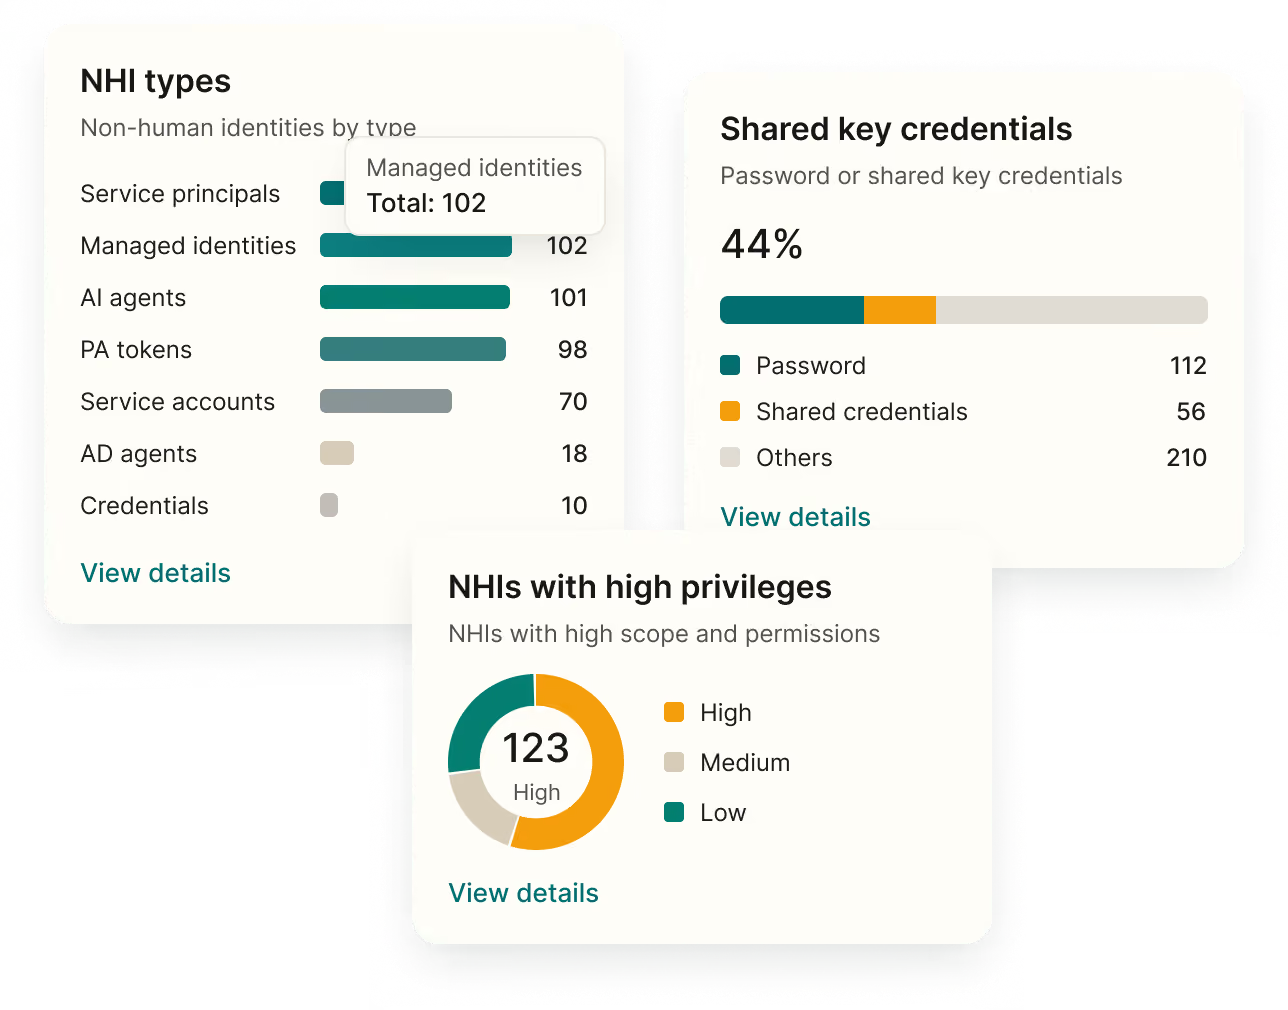
Identity risks pile up unnoticed
Heading
MFA gaps hide in local accounts
Accounts outside SSO skip MFA, and nobody notices.
Settings drift app by app
Every app has its own configuration, and one weak setting is enough.
Findings without fixes
Tools flag issues, then leave the remediation to you.
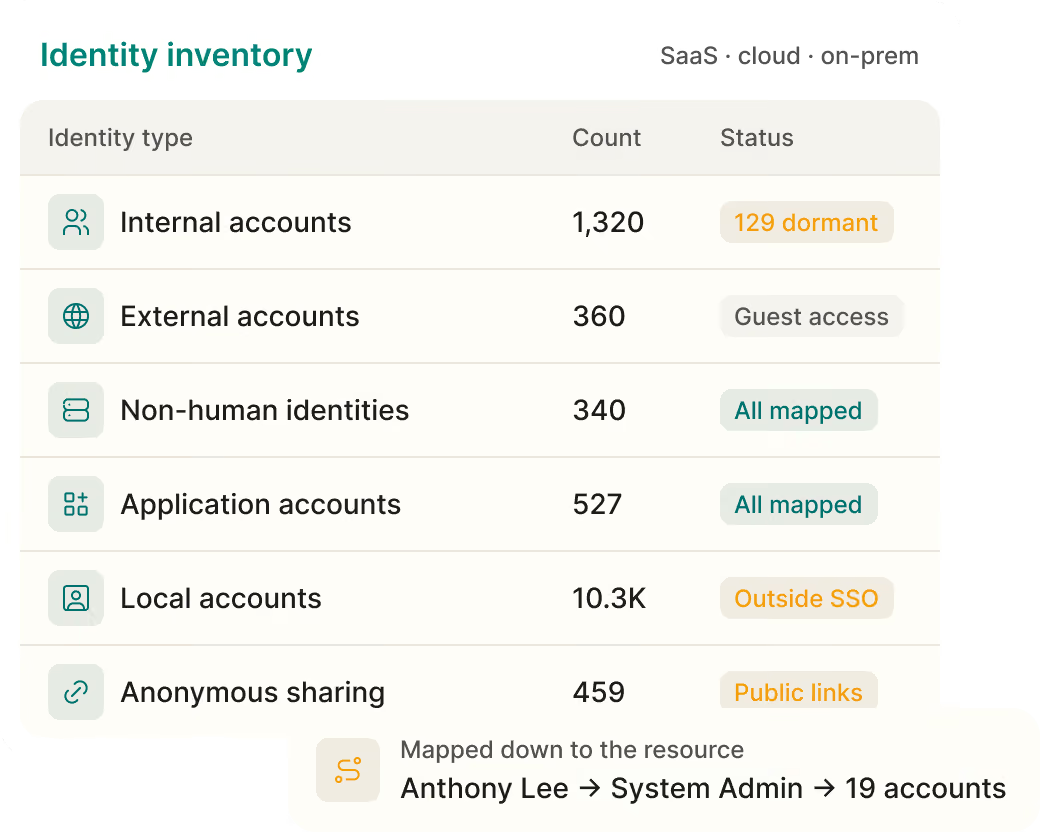
Every identity, permission, and resource

Every kind of identity
Map human identities, NHIs, and AI agents, with their groups and permissions.

Down to the resource
Follow access to the resource across SaaS, cloud, and on-prem.
Close MFA and password gaps

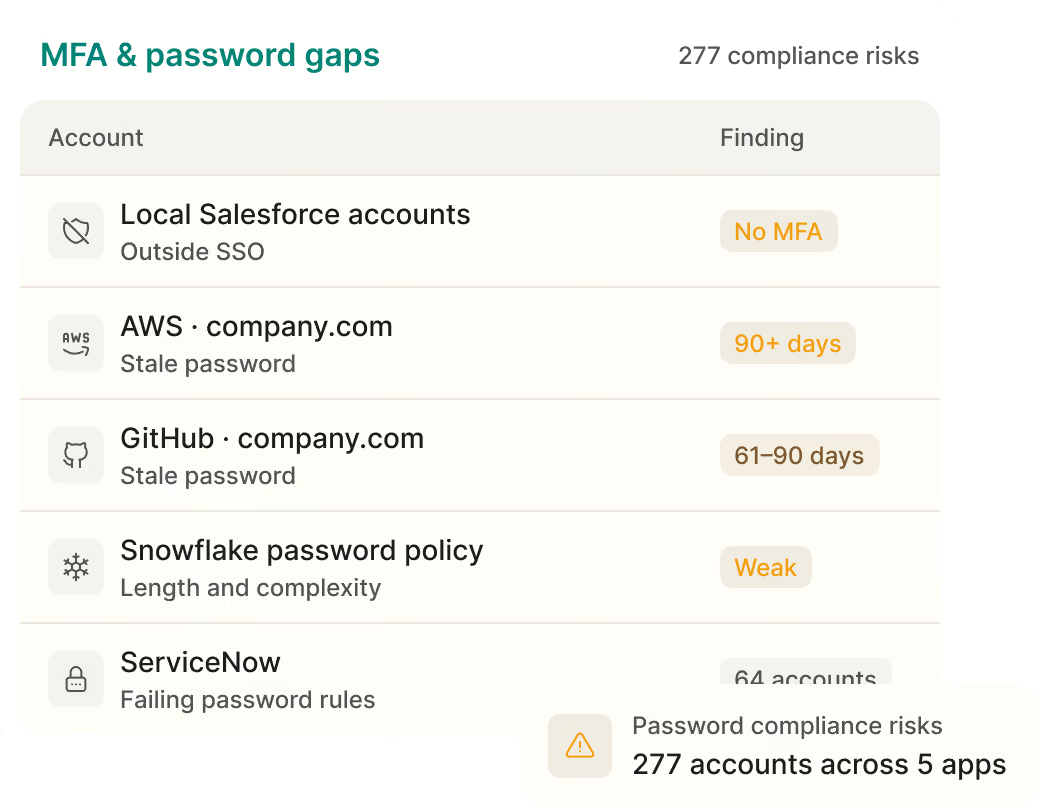
MFA on every account
See MFA status on every account your apps report, including local accounts outside SSO.

Stale and weak passwords
Flag stale passwords and weak password policies.
Catch risky app settings
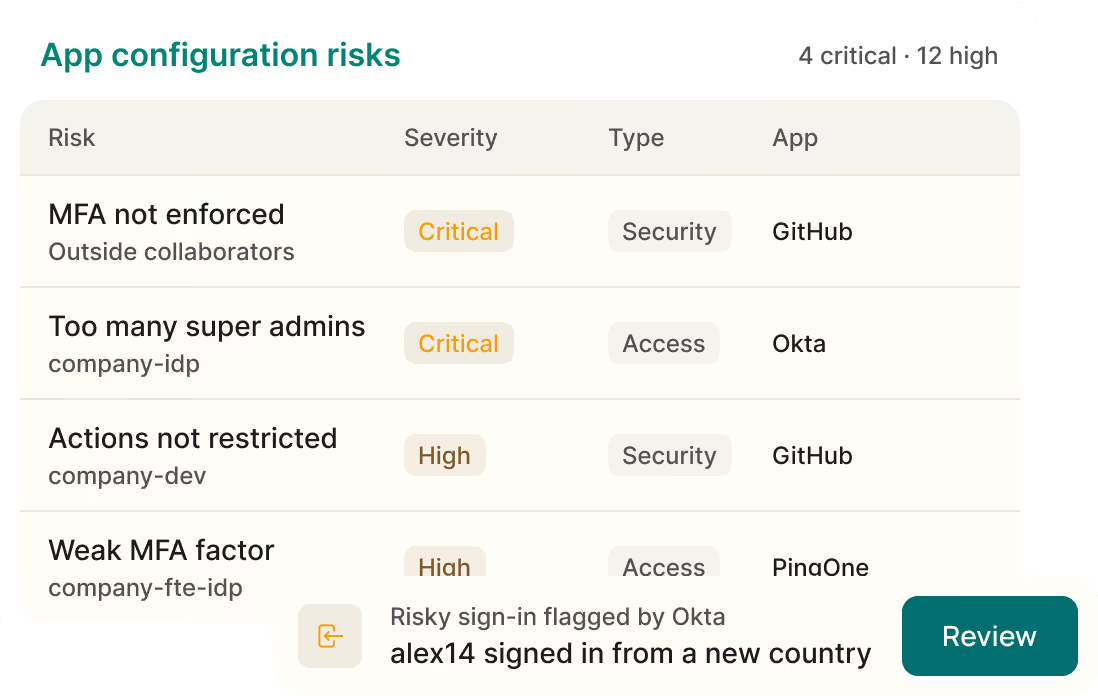
Find risky settings in supported apps, plus risky sign-ins your IdP flags.
MFA that isn’t enforced
Find apps that let users sign in without MFA.

Weak MFA factors
Flag factors that are easier to bypass.
Risky sign-ins
See the risky sign-ins your IdP flags.
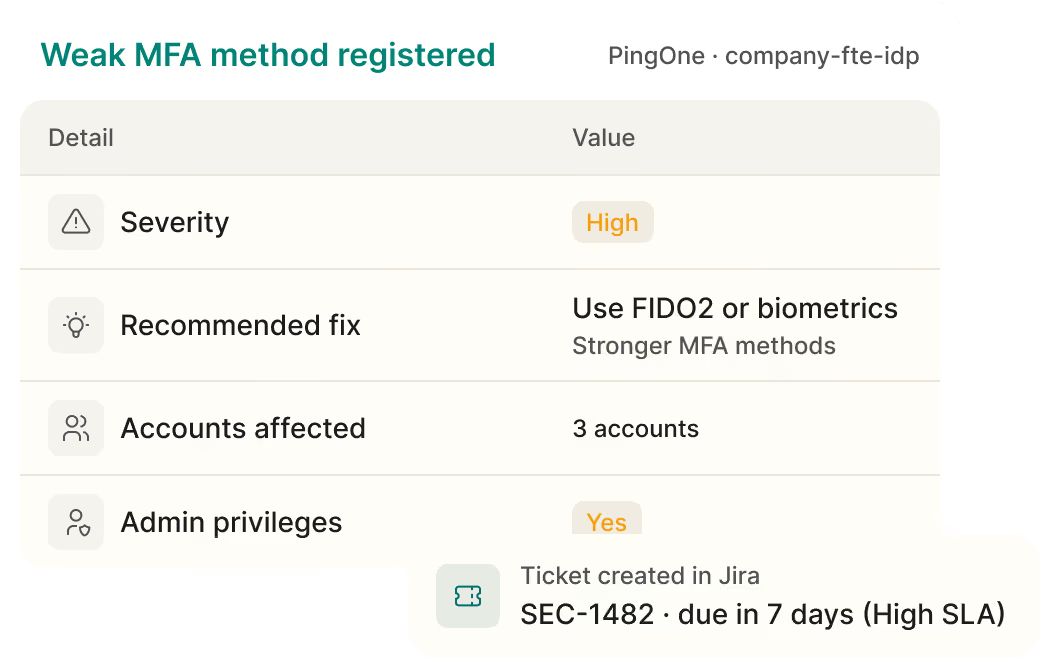
Fix the riskiest findings first
Every finding is ranked by severity with a recommended fix.

Ranked by severity
Critical, high, moderate, or low, each with a recommended fix.

Fix in Oleria or open a ticket
Remediate in Oleria or send a ticket to Jira or ServiceNow.

Tracked against your SLA
Every finding is tracked against the SLA you set for its severity.
Real customers. Real results.
Security teams use Oleria to clean up excess access, get through audits faster, and bring AI agents under control

Oleria is one of those things that once you see it and get it, it’s hard to imagine doing what you’ve been doing without it.
Being able to assess the current state and optimize around least privilege provides the ROI in itself.And the ability to understand what my engineers need will help us provide least- privilege access
Oleria gives us unparalleled visibility into identity access and usage, saving time and strengthening our compliance posture.
Questions about identity security posture management
What is identity security posture management (ISPM)?
Identity security posture management (ISPM) finds and fixes risky identity configurations, such as missing MFA, weak passwords, misconfigured apps, and excess access. Oleria covers human identities, NHIs, and AI agents across SaaS, cloud, and on-prem, and ranks every finding with a recommended fix.
What risks does Oleria find?
Misconfigured access, MFA gaps, SSO gaps, excess permissions, orphaned accounts, shadow IT, and guest account risks, each with context and a recommended fix.
How are findings prioritized?
Each finding is rated critical, high, medium, or low, based on severity, how many identities it affects, and their privilege level. Findings near their SLA deadline are surfaced first.
Can Oleria fix what it finds?
Yes. Fix supported findings directly in Oleria, such as disabling a dormant account or revoking external access, or create a ticket in Jira or ServiceNow.
How is ISPM different from a SIEM or CASB?
A SIEM or CASB watches activity and data movement. ISPM shows who has access and how it’s configured, including local accounts outside SSO, and ranks each finding with a recommended fix.
Learn more about identity posture
Guides, research, and customer stories on identity security posture.