Identity governance for commercial and regional banks
See who can reach customer accounts and financial systems, from staff and vendors to service accounts and AI agents, with proof for exams.
Get a demo
Who has access to customer data across your bank?
One platform for every identity at your bank, with real usage behind each access decision.
Branch and operations staff
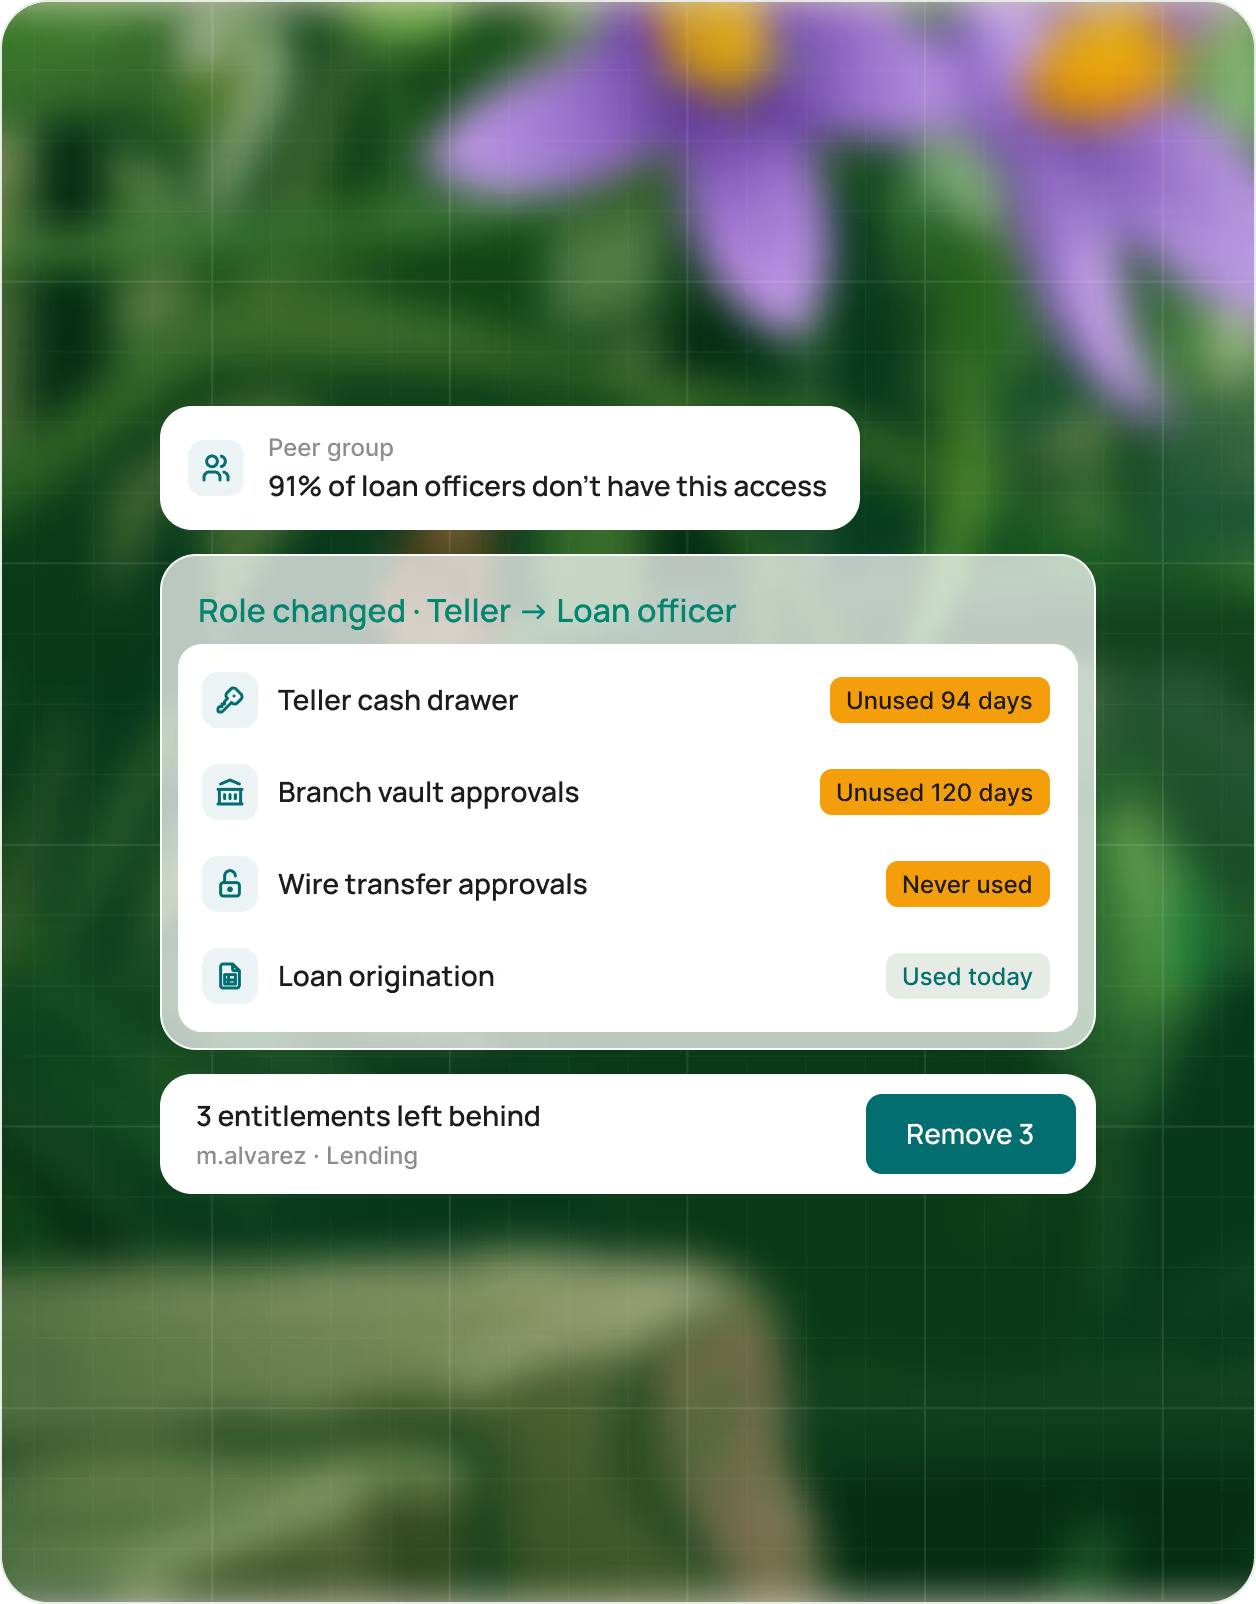
Tellers become loan officers and analysts change teams, and old entitlements stay behind. See what each person uses and remove what their role doesn’t need.
Accounts from acquisitions
Each acquisition brings another directory and its accounts. See them alongside your own, and find the accounts no one owns.
Core providers and fintech partners
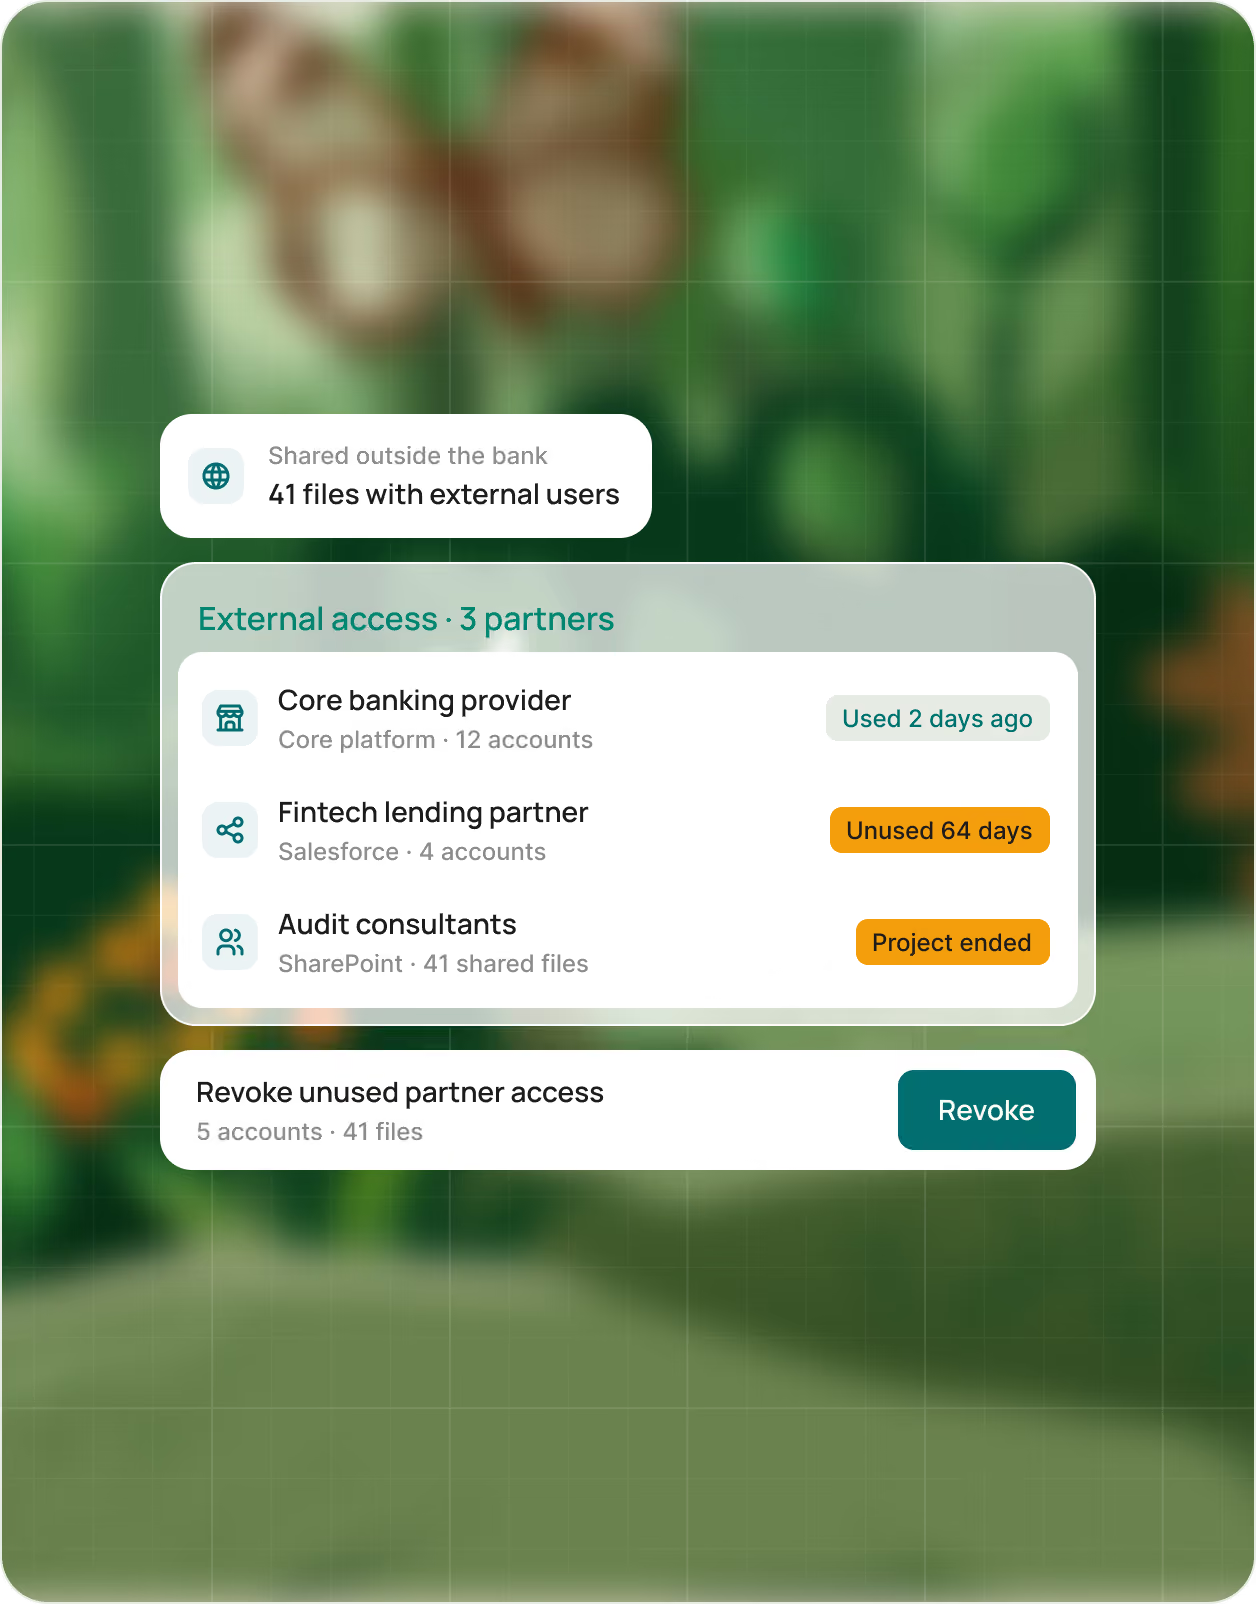
Core providers, fintech partners, and consultants get accounts and shared files. See what each one can reach and revoke access that’s no longer used.
Service accounts and AI agents
Integrations, scripts, and AI agents run on service accounts and tokens. See what each one can reach in your connected systems and who owns it.
Access reviews
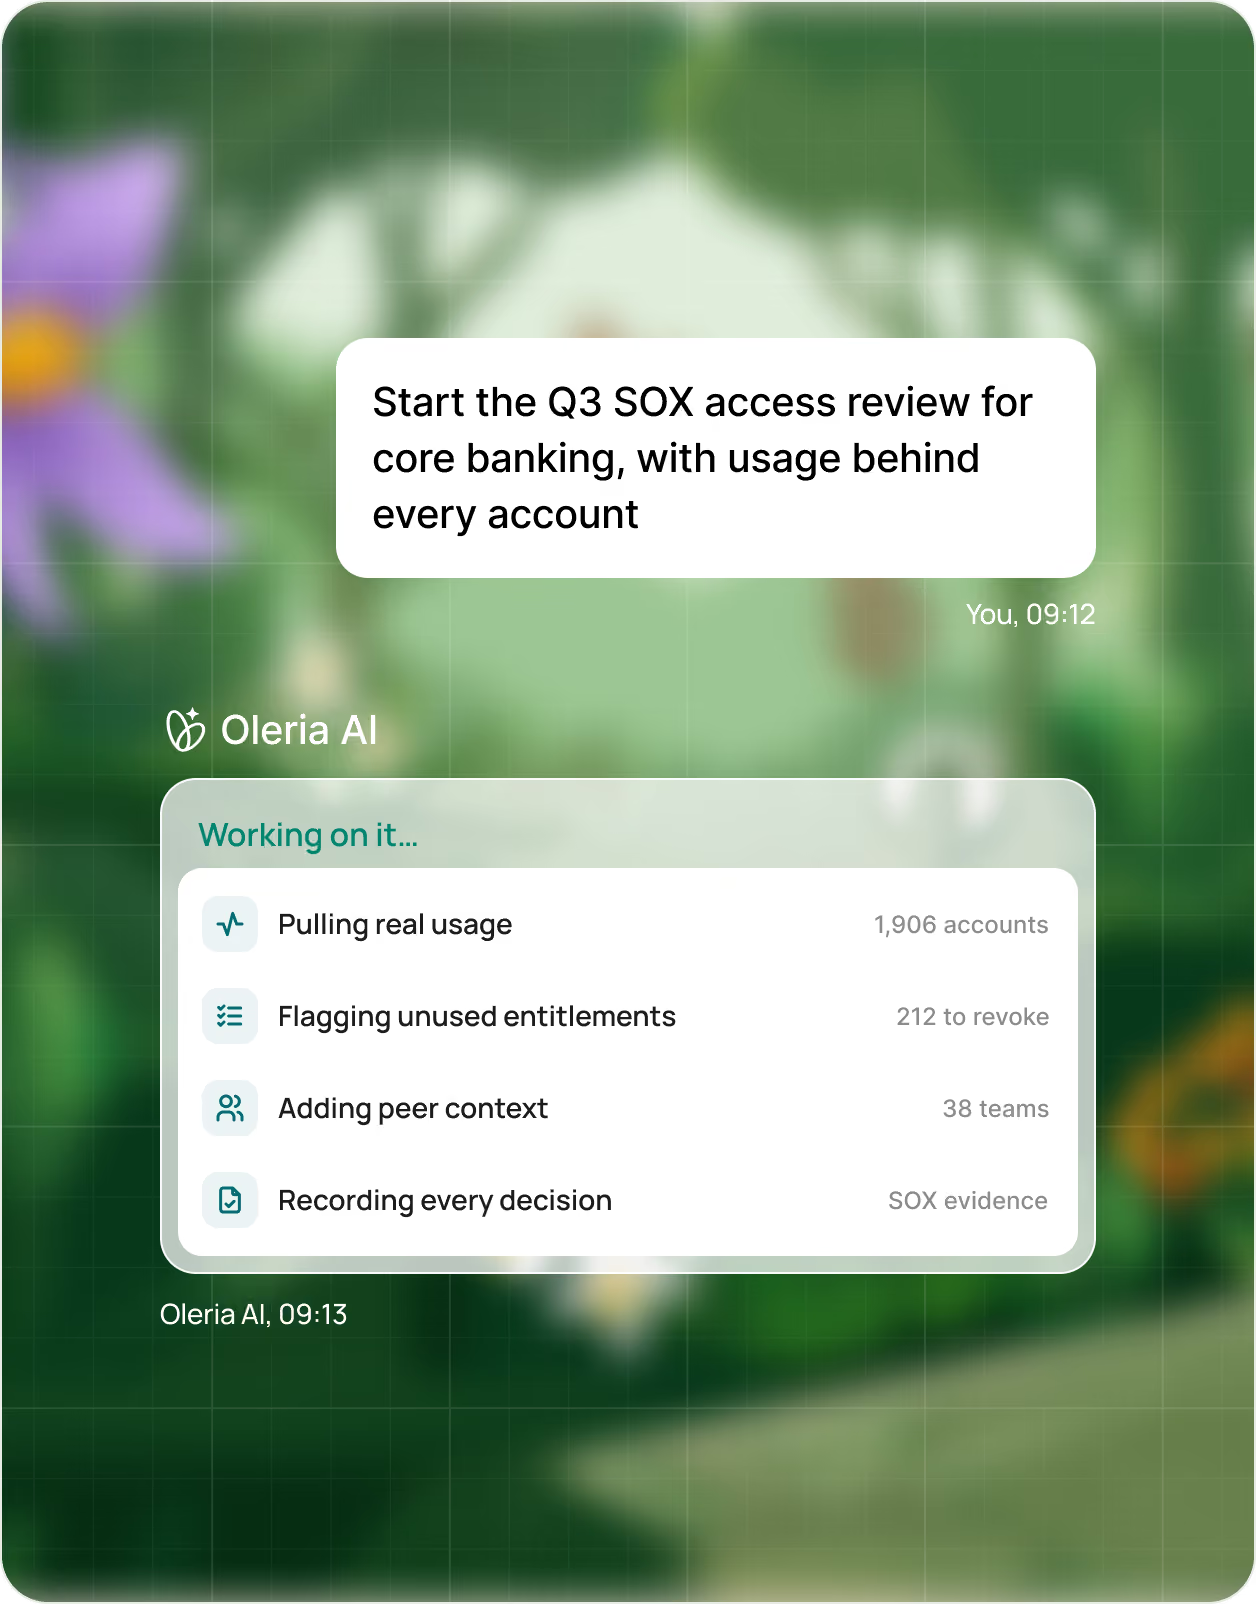
Run SOX and PCI DSS reviews on real usage, with an audit record for every decision.
Least privilege
Remove access left behind by role changes, acquisitions, and departed staff.
External access
See what core providers, fintech partners, and consultants can reach.
MFA & SSO coverage
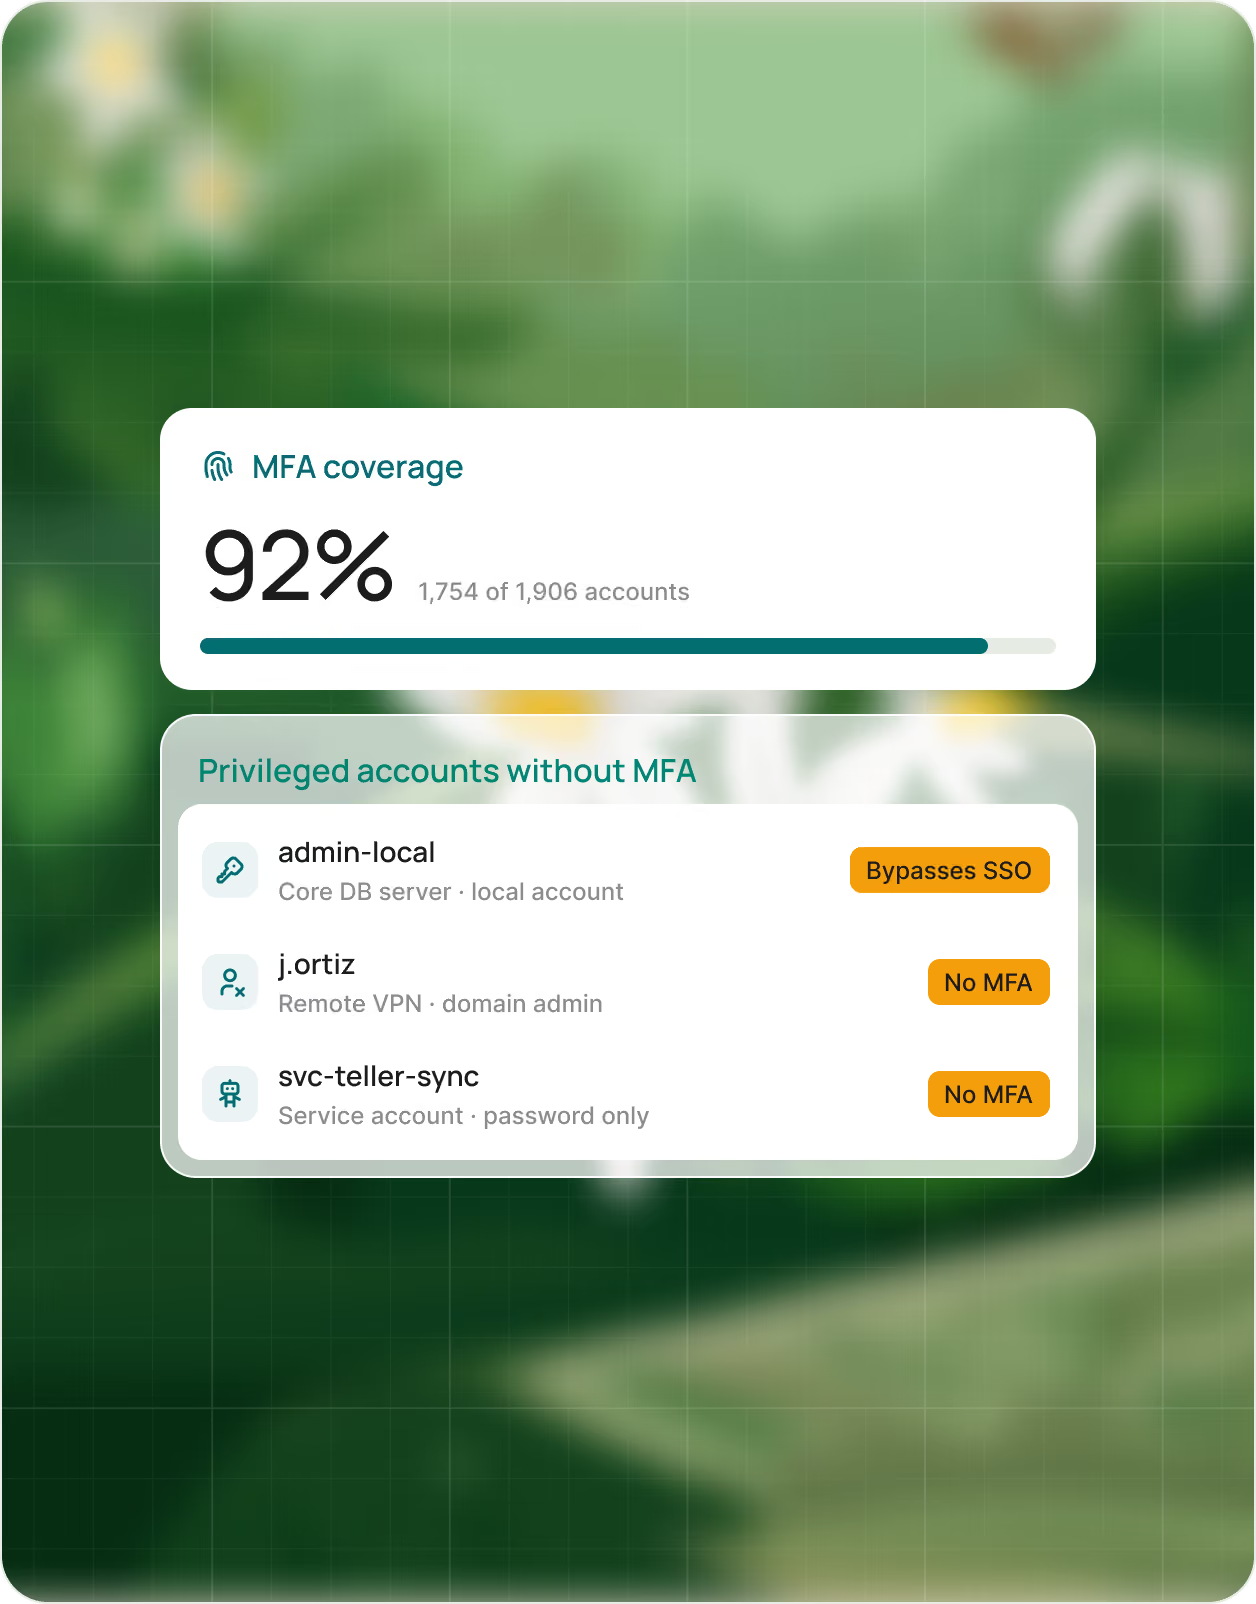
Find privileged and remote accounts without MFA, including local accounts.
Data access governance
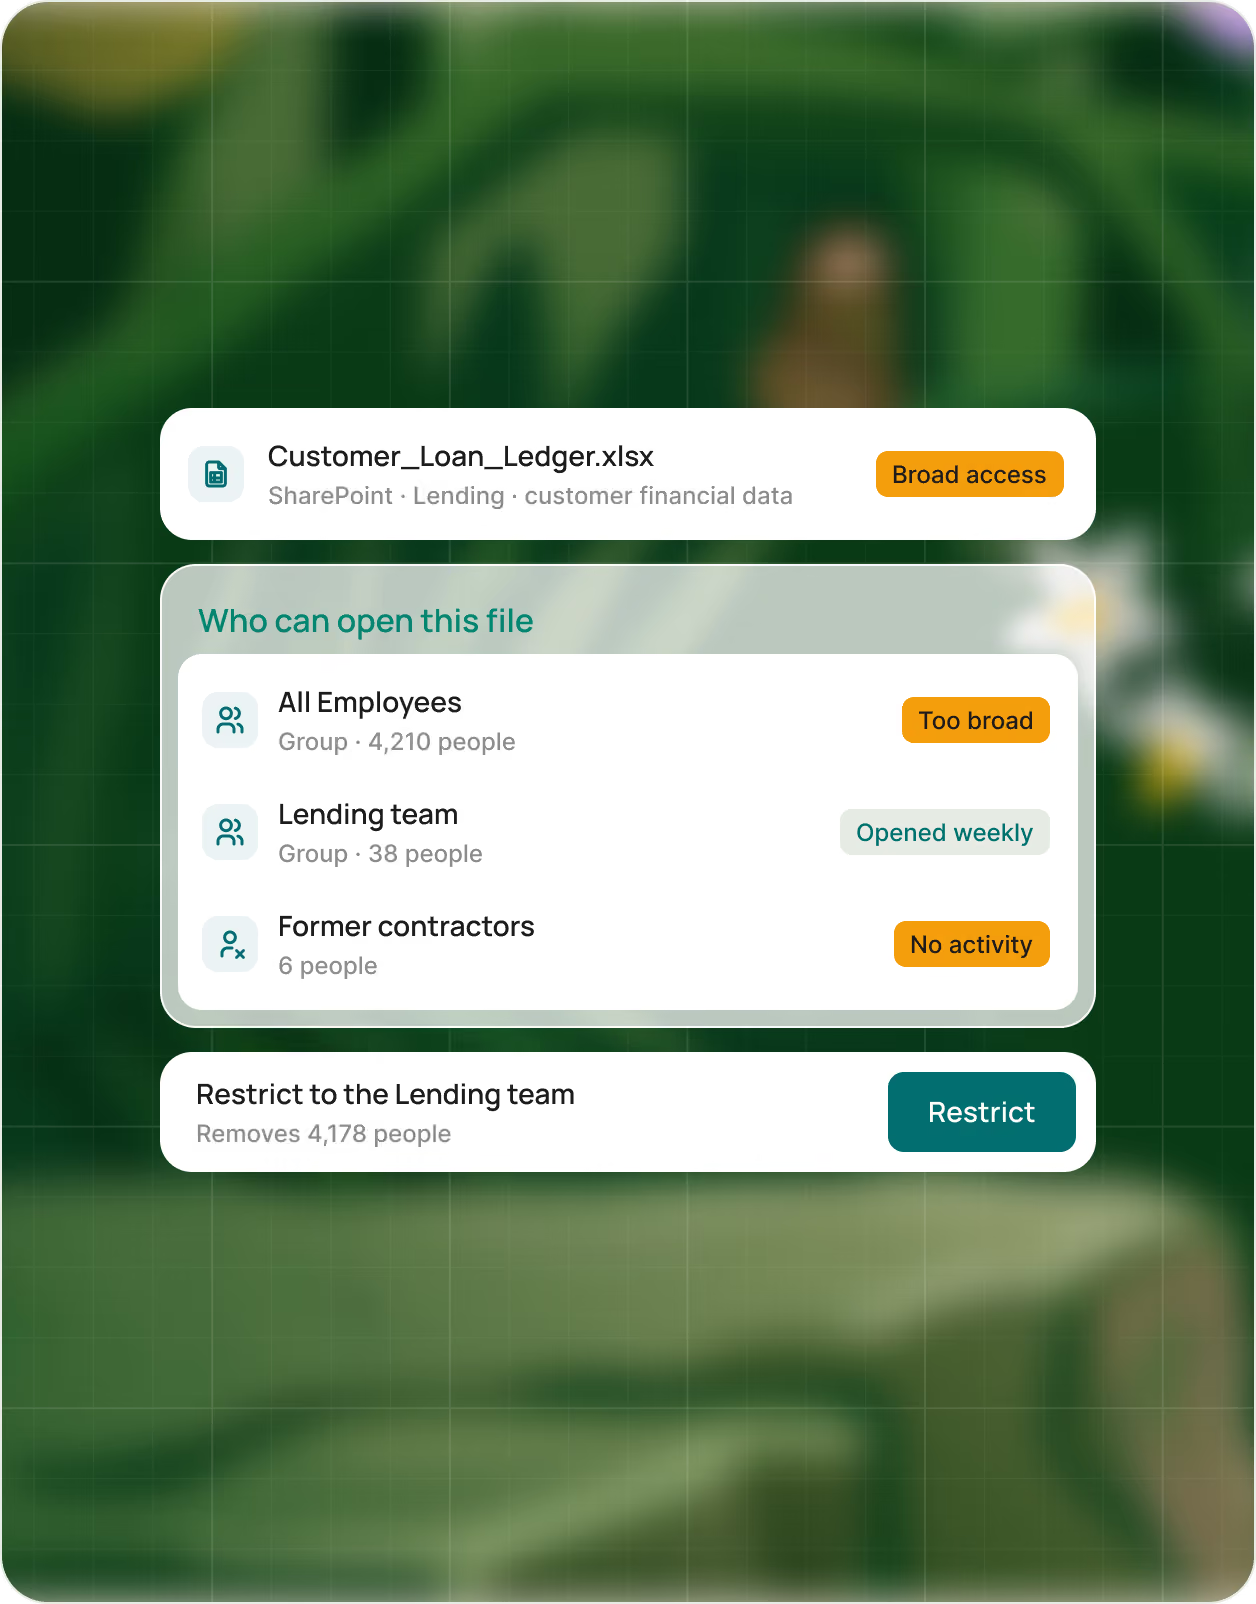
See who can open customer financial data in SharePoint, drives, and Salesforce.
Which banking regulations does Oleria support?
Map each access requirement to the evidence your auditors and examiners ask for.
Questions about identity governance for banking
What is identity governance for banking?
Oleria MCP is an MCP server for identity governance. It lets the AI assistants, coding agents, and custom copilots your team already uses query and reason over your identity estate in natural language. No SDK, no new framework, no rebuilt workflows: if your client speaks MCP, it works with Oleria.
Identity governance for banking is how banks control who can access customer accounts, financial systems, and sensitive data. It covers employees, vendors, fintech partners, service accounts, and AI agents, and produces the access reviews and evidence that examiners and SOX auditors ask for.
How does Oleria help banks prepare for exams?
Most platforms layer AI on top of tools designed for static rules and periodic reviews. Oleria AI was designed into Trustfusion from the data layer up — a live identity graph continuously enriched with usage, peer, risk, and authentication context, with Oleria AI's reasoning running as a first-class capability across every workflow on the platform. That foundation is what makes recommendations accurate instead of approximate, and what makes a platform-level MCP endpoint possible.
Oleria shows who can access what across your connected systems, based on real usage. Teams run access reviews with context for each decision, remove unused access with a justification, and export the record examiners and auditors ask for
Does Oleria support PCI DSS access reviews?
No. Oleria AI is the intelligence built into the Trustfusion platform you already know. The naming gives a clear identity to a capability that spans every workflow on the platform, governance, risk, investigations, access, and the MCP endpoint rather than presenting AI as a separate SKU or a bolt-on feature.
Yes. PCI DSS asks you to review all user accounts, including vendor accounts, at least once every six months. Oleria runs reviews with usage and peer context for each account and keeps a record of every decision.
How does Oleria govern vendor and fintech partner access?
The MCP (Model Context Protocol) endpoint exposes Oleria AI's reasoning and graph to any MCP-compatible client — Claude, ChatGPT, your internal copilots, or custom agents. Teams can query Oleria in natural language ("show me everyone with prod AWS access who hasn't logged in for 30 days"), pull context into agentic SOC and IAM workflows, and use the result inside the tools they already trust. The endpoint is read-only by design: agents reason.
Oleria shows external users and shared files across your connected apps, what each one can reach, and when it was last used. You can revoke access that is no longer needed in supported apps, with an audit record.
Can Oleria handle accounts from acquired banks?
Access reviews and provisioning, external access oversight, risk monitoring, incident investigations, unused and unintended access detection, and authentication posture monitoring. The same unified graph and Oleria AI reasoning underpin every one of them — which is what makes Trustfusion feel like one platform rather than a suite of point tools.
Yes. Connect the acquired bank's directory and apps, such as Active Directory or Entra ID, and Oleria shows its accounts and access alongside yours, including accounts with no owner and access no one uses.
Learn more about identity governance for banking
Customer stories and guides on meeting SOX, FINRA, and GLBA access requirements with less manual work.