Identity governance for technology and SaaS companies
See who can reach your code, cloud, and customer data, across engineers, contractors, SaaS apps, service accounts, and AI agents.
Get a demo
Who has access across your SaaS and cloud stack?
Govern every identity across your SaaS, cloud, and developer tools, based on what each one actually uses.
Engineers with admin access
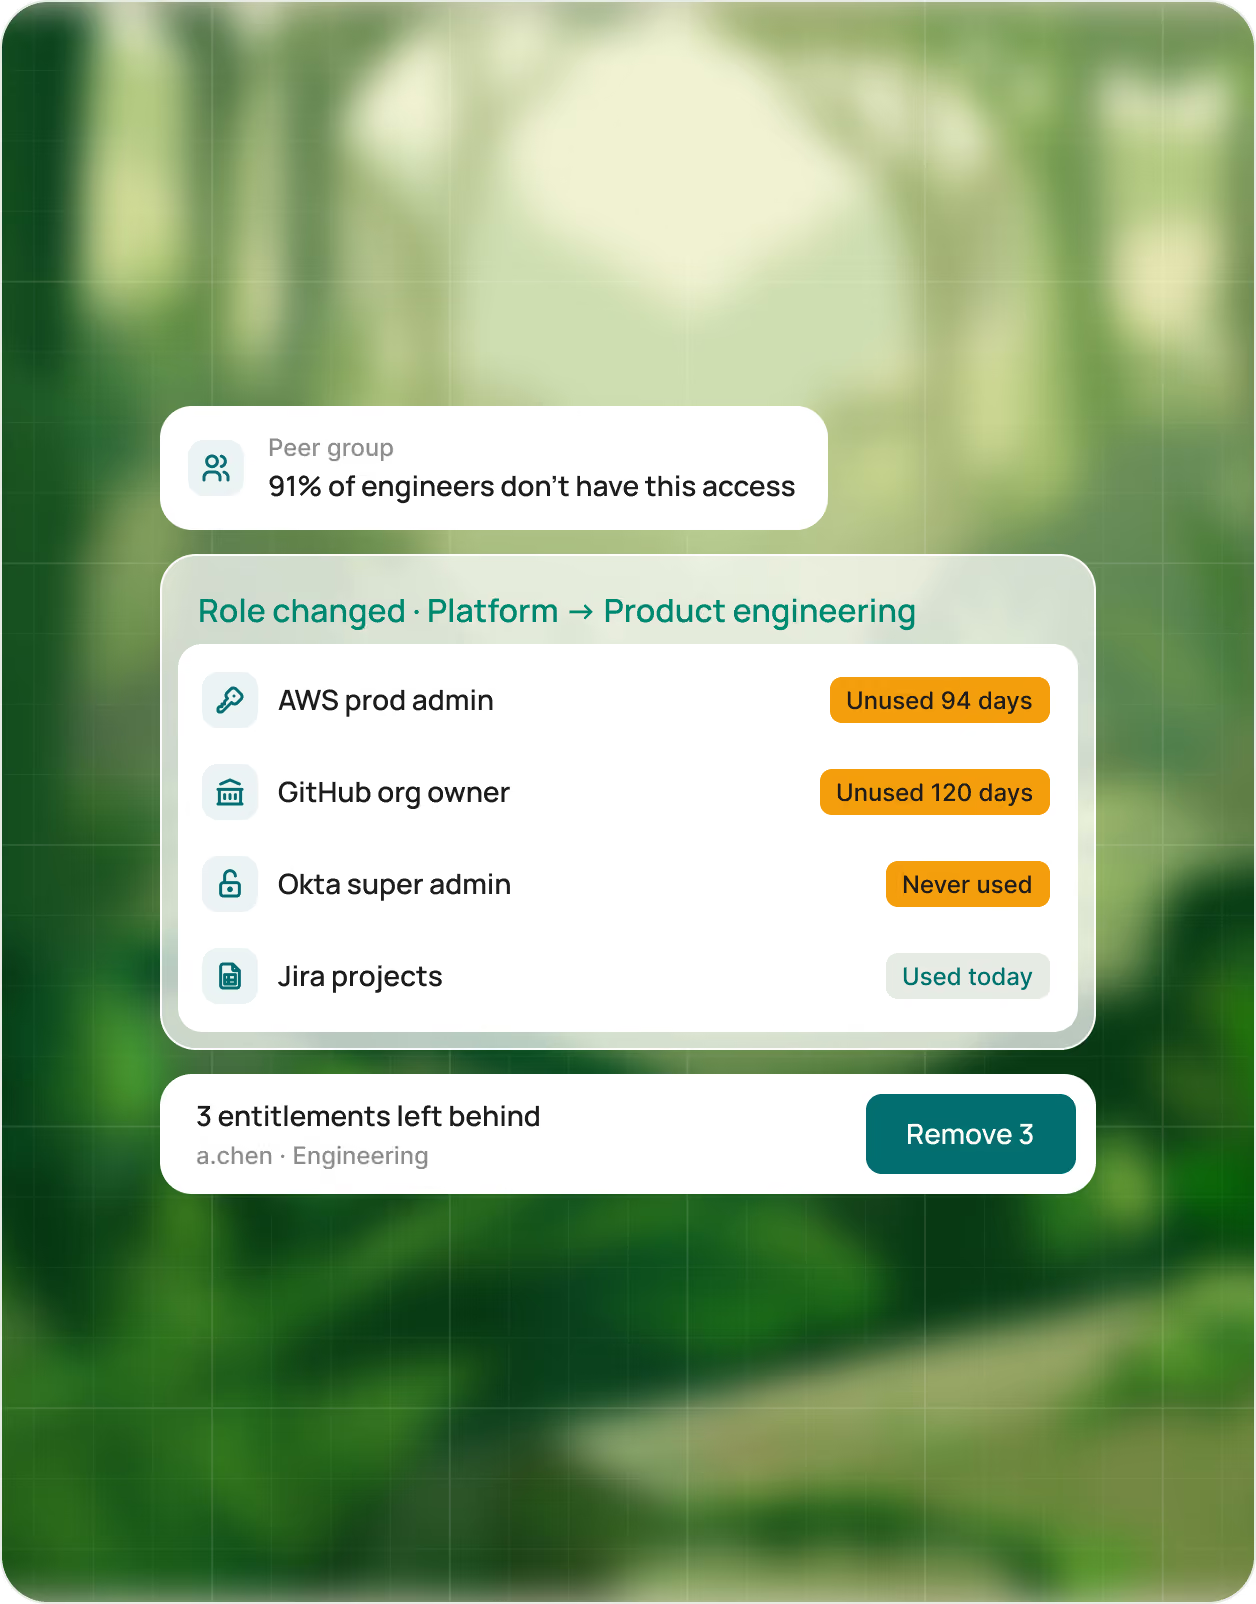
Engineers pick up admin rights in cloud and code as projects change. See what each person still uses and remove standing access they don't need.
Contractors and partners
Contractors and implementation partners join fast and leave quietly. See what each one can reach, and end access when the engagement ends.
Apps teams adopt on their own
Teams sign up for SaaS and AI tools with company accounts. See which apps connect to your data through OAuth, and who uses them.
Service accounts and AI agents
CI/CD pipelines, integrations, and AI agents run on service accounts and tokens. See what each one can reach and who owns it.
Least privilege
Remove unused admin rights in cloud and code, based on what engineers actually use.
Access reviews
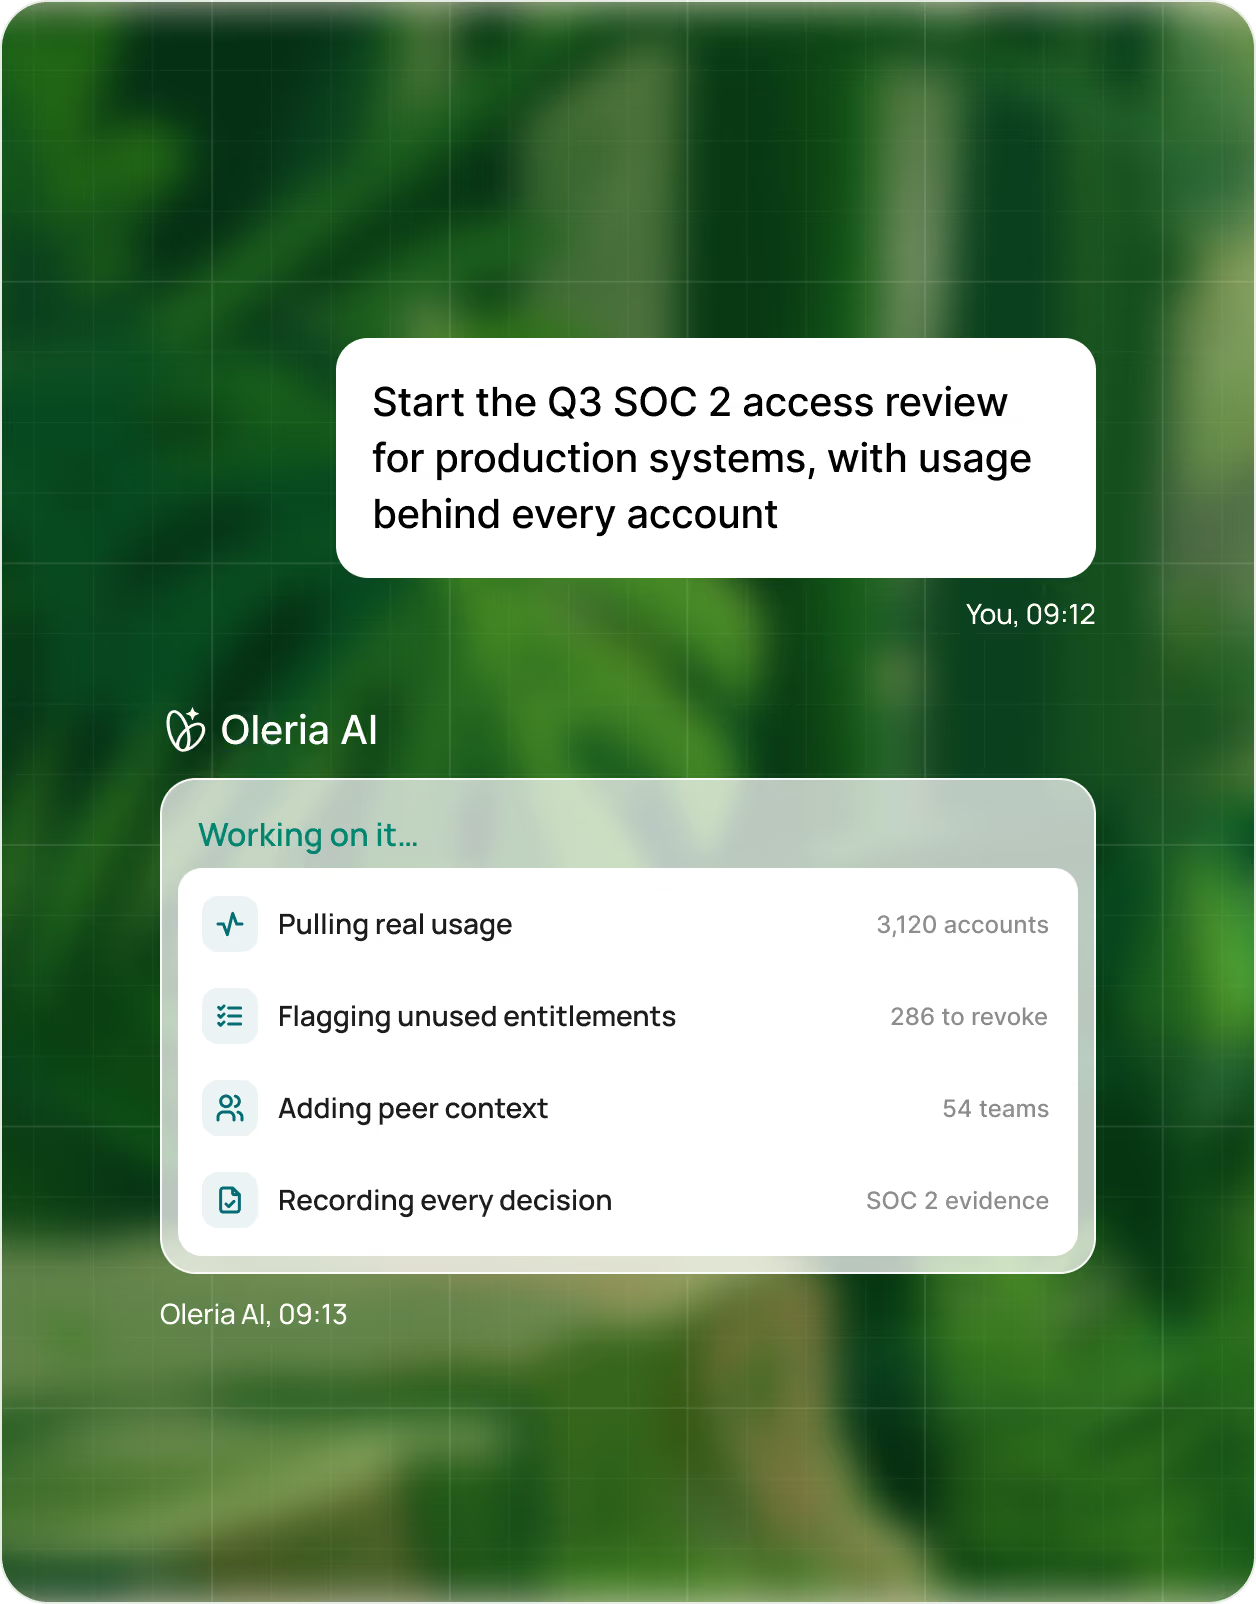
Run SOC 2 and ISO 27001 reviews on real usage, with a record of every decision.
Secure AI adoption
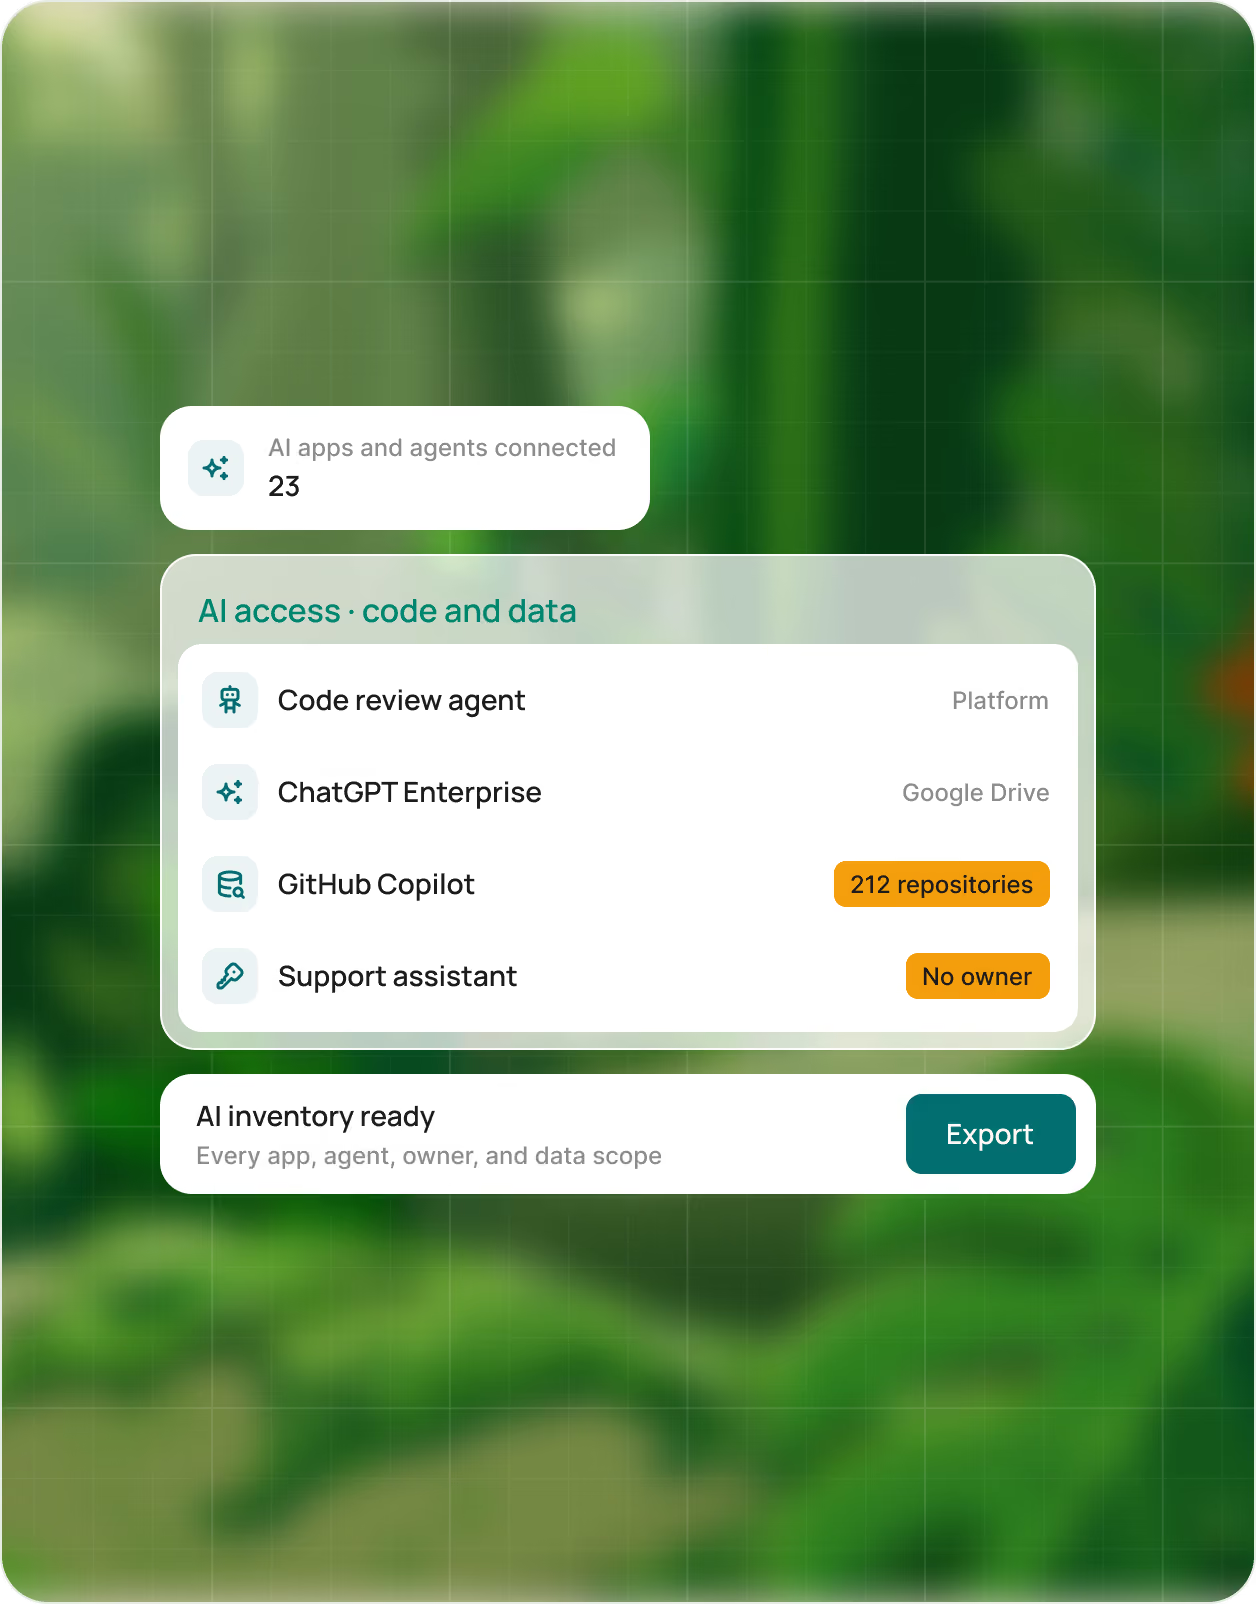
See which AI apps and agents connect to your code and data, and who owns each one.
External access
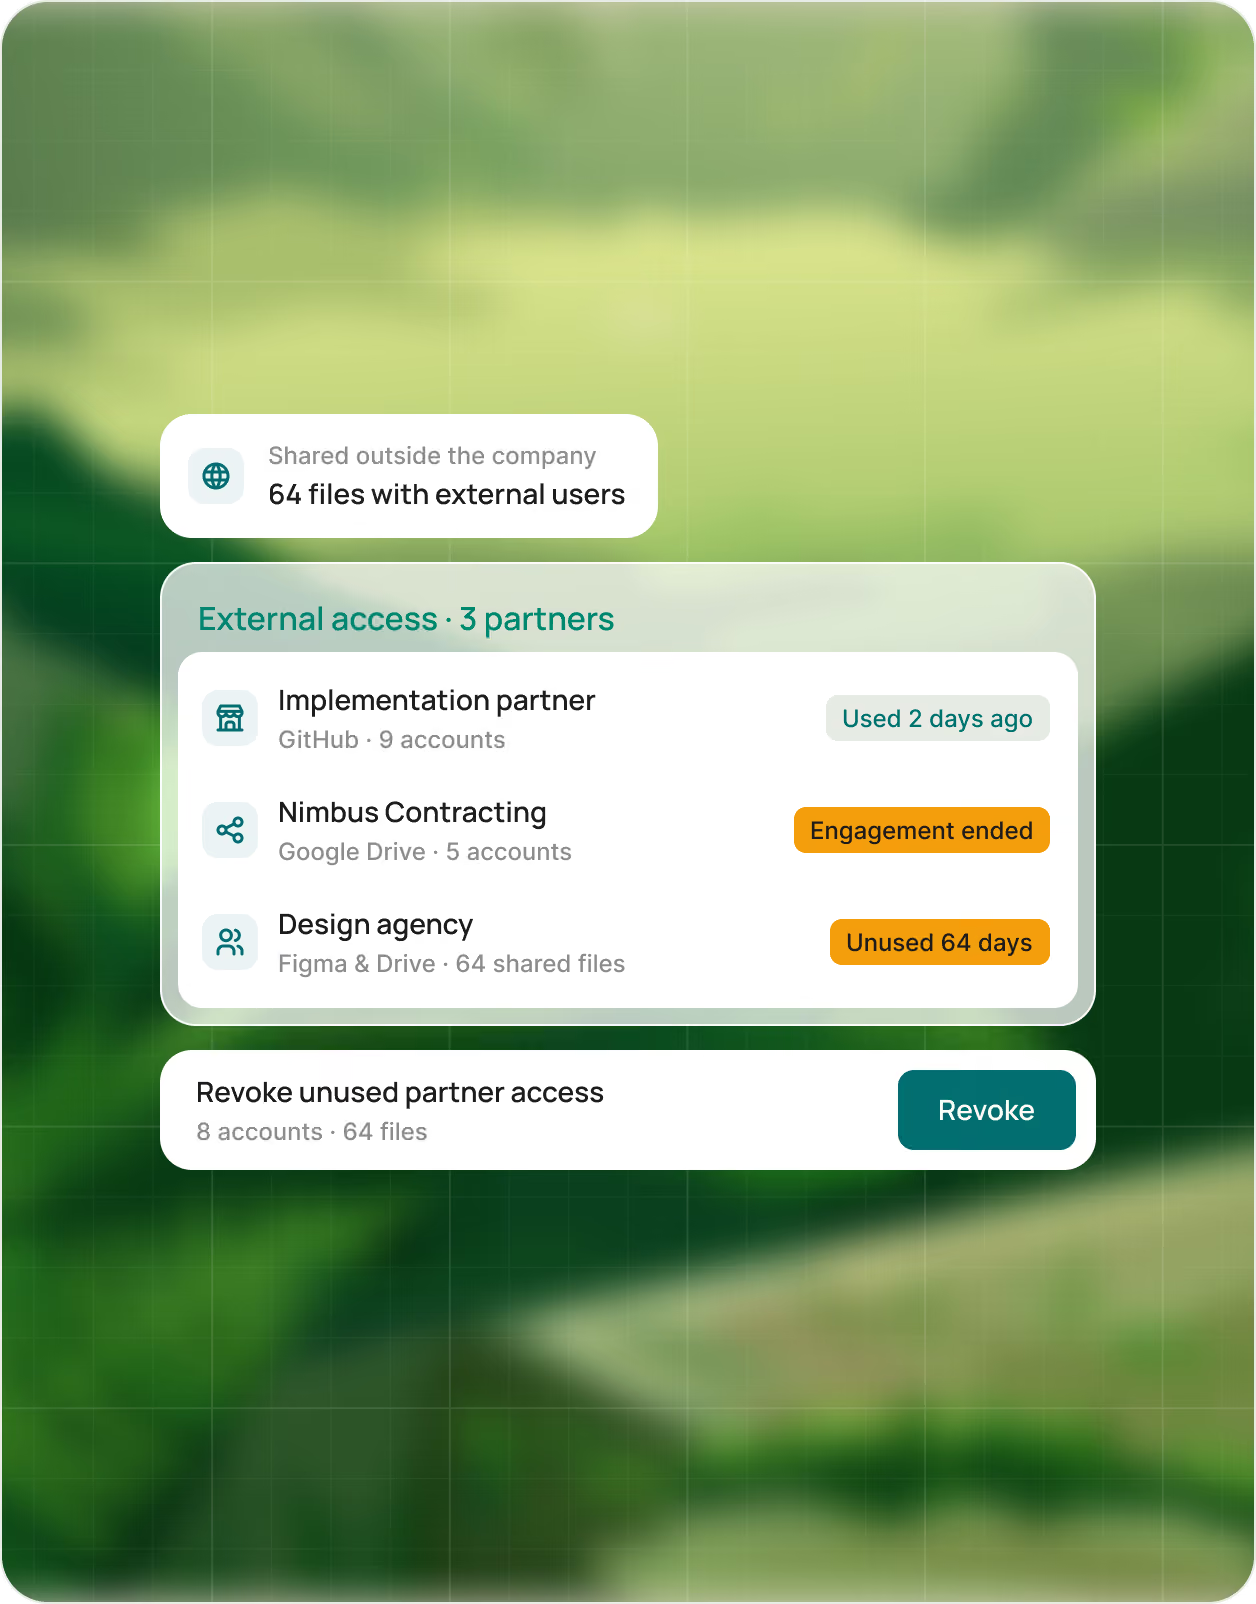
Find repositories, files, and records shared with contractors and outside accounts.
Identity risk monitoring
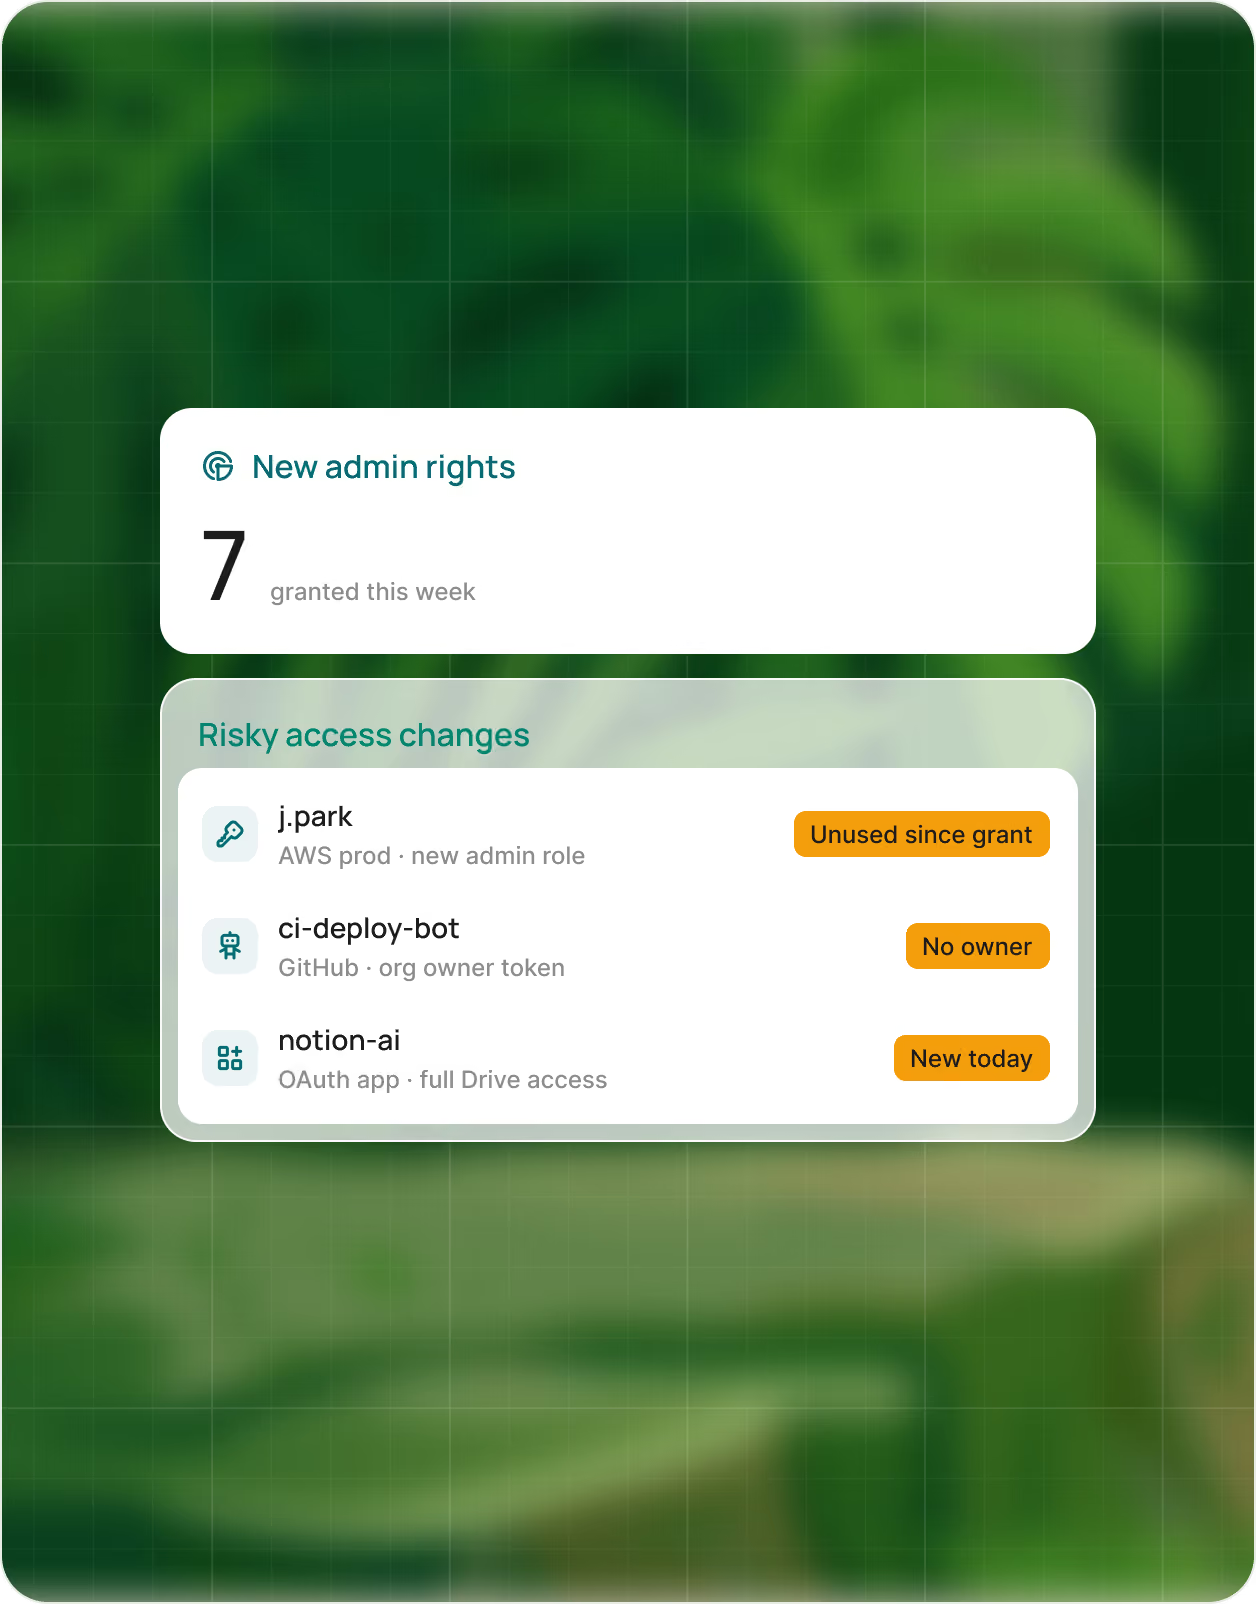
Catch new admin rights and risky access as your team and stack grow.
Incident investigations
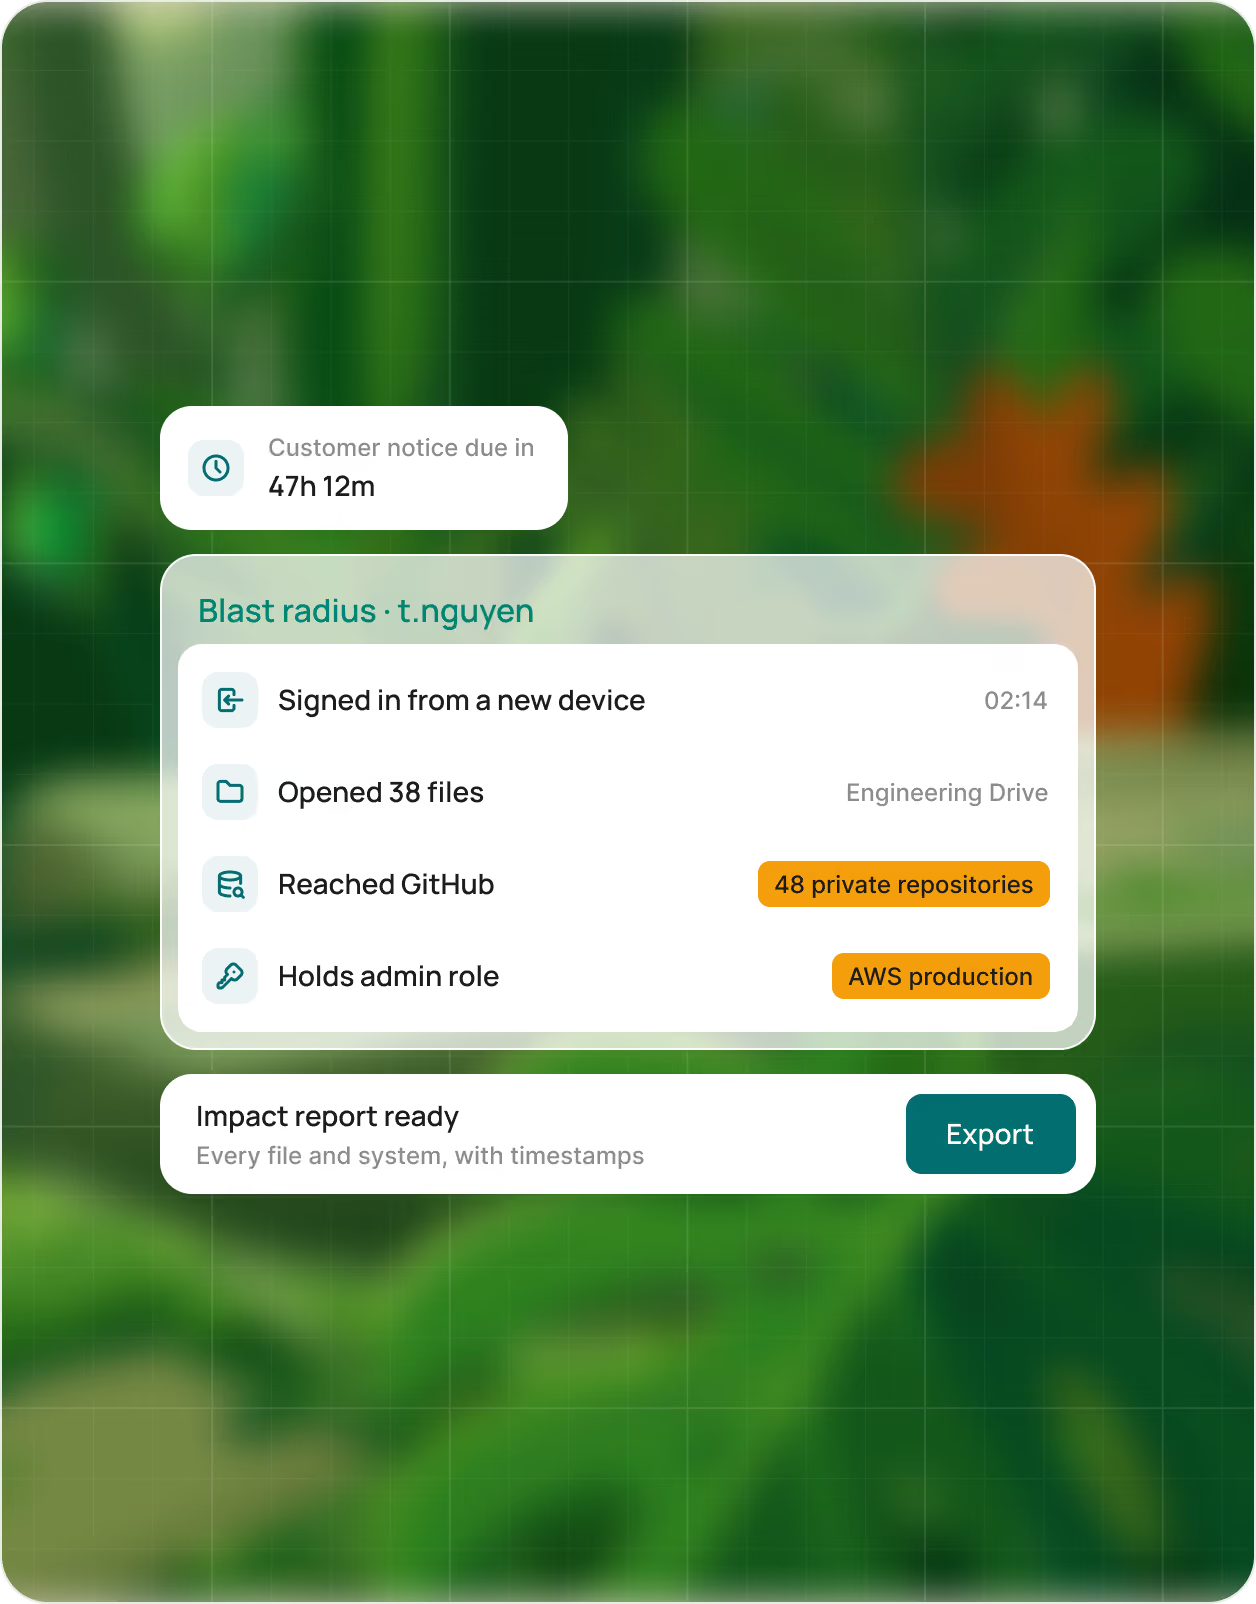
See what a compromised account could reach, down to each file.
Which compliance frameworks does Oleria support?
Map each access control to the evidence your auditors and enterprise customers ask for.
Questions about identity governance for technology
What is identity governance for technology companies?
Oleria MCP is an MCP server for identity governance. It lets the AI assistants, coding agents, and custom copilots your team already uses query and reason over your identity estate in natural language. No SDK, no new framework, no rebuilt workflows: if your client speaks MCP, it works with Oleria.
Identity governance for technology companies is how software and SaaS businesses control who can access their code, cloud, and customer data. It covers engineers, contractors, SaaS and AI apps, service accounts, and AI agents, and produces the access reviews that SOC 2 and ISO 27001 audits ask for.
How does Oleria help with SOC 2 access reviews?
SOC 2 auditors look for access that is authorized, reviewed, and removed when no longer needed. Oleria runs access reviews with usage and peer context for each account, records every decision, and removes unused access with a justification.
Does Oleria cover cloud and developer tools?
Yes. Oleria connects to your identity provider, cloud platforms, and developer tools such as GitHub, and shows who can reach what in each, alongside how that access is actually used.
Yes. Oleria connects to your identity provider, cloud platforms, and developer tools such as GitHub, and shows who can reach what in each, alongside how that access is actually used.
How does Oleria find SaaS and AI apps teams adopt on their own?
The MCP (Model Context Protocol) endpoint exposes Oleria AI's reasoning and graph to any MCP-compatible client — Claude, ChatGPT, your internal copilots, or custom agents. Teams can query Oleria in natural language ("show me everyone with prod AWS access who hasn't logged in for 30 days"), pull context into agentic SOC and IAM workflows, and use the result inside the tools they already trust. The endpoint is read-only by design: agents reason.
Oleria discovers the OAuth apps connected to your company accounts, including AI tools, and shows what data each one can reach, who uses it, and when it was last used.
How does Oleria govern contractor access?
Access reviews and provisioning, external access oversight, risk monitoring, incident investigations, unused and unintended access detection, and authentication posture monitoring. The same unified graph and Oleria AI reasoning underpin every one of them — which is what makes Trustfusion feel like one platform rather than a suite of point tools.
Oleria shows what each contractor can reach across your connected apps, when it was last used, and what has been shared with them. When an engagement ends, you can find and remove the access left behind.
Learn more about identity governance for technology
Customer stories and guides on governing access across fast-moving SaaS, cloud, and code.