MFA & SSO Coverage
Find every MFA and SSO gap, including local accounts
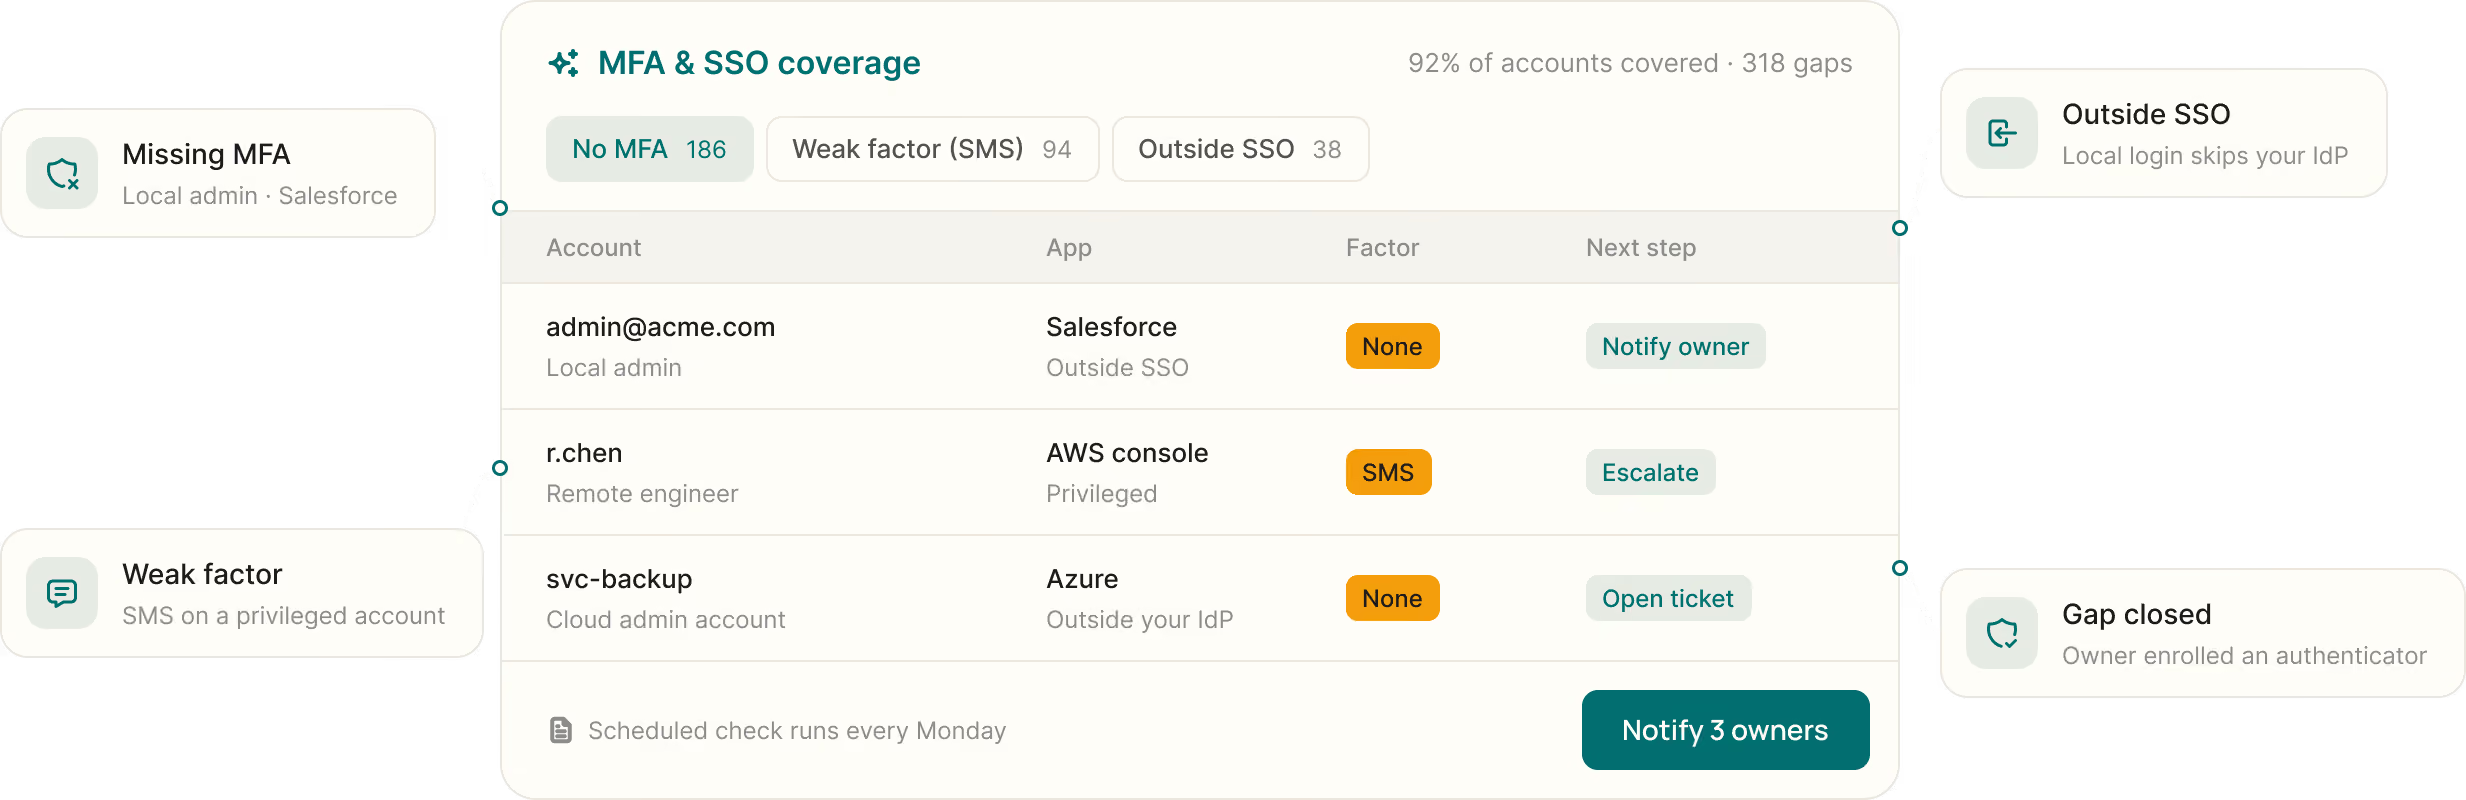
See which accounts lack MFA, rely on weak factors like SMS, or sign in outside your SSO, then drive each open gap to closure.
Where are your MFA and SSO gaps hiding?
99%
Local accounts bypass SSO
Admins keep local logins in SaaS apps that never pass through your IdP.
Weak factors count as MFA
SMS codes pass the MFA check but are easier to intercept than app or key-based factors.
Every app reports differently
Each app tracks MFA its own way, so coverage gets checked by hand.
How Oleria closes MFA and SSO gaps

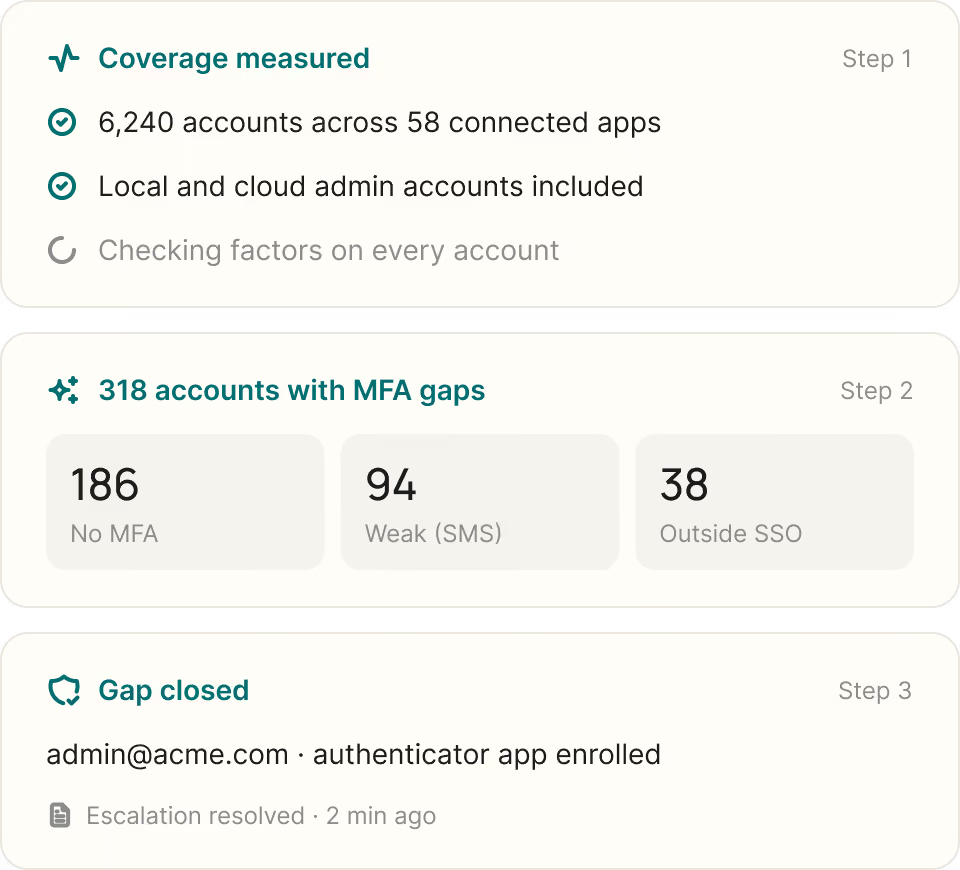
Measure coverage
See MFA status and SSO use for every account, including local and cloud admin accounts outside your IdP.

Find weak and missing MFA
Flag accounts with no MFA or weak methods such as SMS, with admin rights and dormancy in view.

Escalate until fixed
Schedule checks, notify account owners, escalate to managers when gaps stay open, or open a ticket.
What does Oleria include for MFA and SSO coverage?
Coverage per account
MFA status and SSO use, including local and cloud admin accounts.
Weak-factor flags
Accounts relying on SMS or other weak methods.
Scheduled checks
Recurring checks that notify account owners.
Escalation and tickets
Escalate to managers or open a ticket in your ITSM tool.
Real customers. Real results.
Security teams use Oleria to clean up excess access, get through audits faster, and bring AI agents under control

Oleria is one of those things that once you see it and get it, it’s hard to imagine doing what you’ve been doing without it.
Being able to assess the current state and optimize around least privilege provides the ROI in itself.And the ability to understand what my engineers need will help us provide least- privilege access
Oleria gives us unparalleled visibility into identity access and usage, saving time and strengthening our compliance posture.
Questions about MFA and SSO coverage
What is MFA coverage?
MFA coverage is the share of accounts that are protected by multi-factor authentication, across every app and identity provider. Oleria measures it for each account, including local accounts outside SSO, and shows which ones are missing MFA or use a weak method.
Why do local accounts bypass SSO?
Many SaaS and cloud apps let admins create accounts with their own username and password. Those logins never pass through your identity provider, so SSO and IdP MFA policies don't apply to them.
Is SMS a weak MFA factor?
No. Oleria AI is the intelligence built into the Trustfusion platform you already know. The naming gives a clear identity to a capability that spans every workflow on the platform, governance, risk, investigations, access, and the MCP endpoint rather than presenting AI as a separate SKU or a bolt-on feature.
SMS is weaker than authenticator apps or security keys because codes can be intercepted or redirected through SIM swapping. NIST classifies SMS as a restricted authenticator. Phishing-resistant factors such as security keys are stronger. Oleria flags accounts that rely on SMS.
Does Oleria enforce MFA?
Oleria finds MFA and SSO gaps and drives them to closure. It runs scheduled checks, notifies account owners, escalates to managers when gaps stay open, and can open tickets in your ITSM tool.
Which compliance frameworks does this help with?
MFA and SSO coverage evidence from Oleria supports authentication controls in PCI DSS, NIST 800-171, HIPAA, SOX, GDPR, and FedRAMP programs.
Learn more about MFA & SSO coverage
Guides and research on closing MFA gaps, weak factors, and accounts that bypass SSO.