The identity governance platform
See Every Identity. Govern Every Access.
Discover every identity, understand who has access to what, and enforce least-privilege governance across human, non-human identities, and AI agents.


Trusted by security leaders worldwide. Built by practitioners. Backed by Evolution Equity Partners, Salesforce Ventures, and Zscaler.
Oleria is one of those things that once you see it and get it, it’s hard to imagine doing what you’ve been doing without it.
of access
Managed security provider
Being able to assess the current state and optimize around least privilege provides the ROI in itself. And the ability to understand what my engineers need will help us provide least-privilege access.
insights
Every identity.
One governance platform.
Human identities
Access piles up with every project and role change, and reviews rarely catch it. Oleria shows what each person actually uses, so you can remove the rest and give reviewers facts instead of guesswork.
Explore human identity governance →
Non-human identities
Service accounts, API keys, and tokens take minutes to create and years to forget. Oleria finds every one, including those nobody registered, and gives each an accountable owner, so no credential keeps access after its purpose ends.
Explored Non-human identity governance →
AI identities
AI agents often act with the access of whoever called them. Oleria gives every agent a human sponsor and shows what it can reach through that delegation, so you can say yes to AI without losing control of access.
Explore AI agent governance →Who has access to this, and should they?
Ask Oleria AI. It answers from your real access and usage data, and explains each answer.
Map every identity, understand the risk, and fix it with confidence
Unified access graph

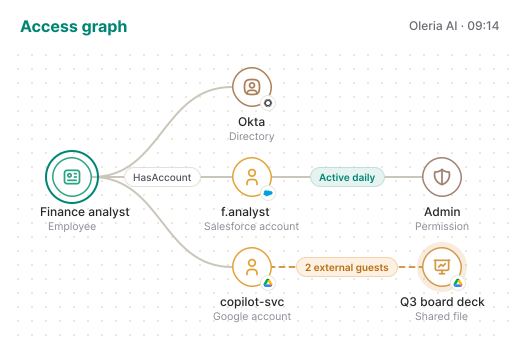
One graph for every identity
Human, non-human, and AI identities across on-prem, cloud, SaaS, and custom apps.

Real usage on every entitlement
Know whether access is actively used, or dormant and for how long.

External access in view
See every contractor, partner, and guest with access, and what’s shared outside the company.
Contextual recommendations

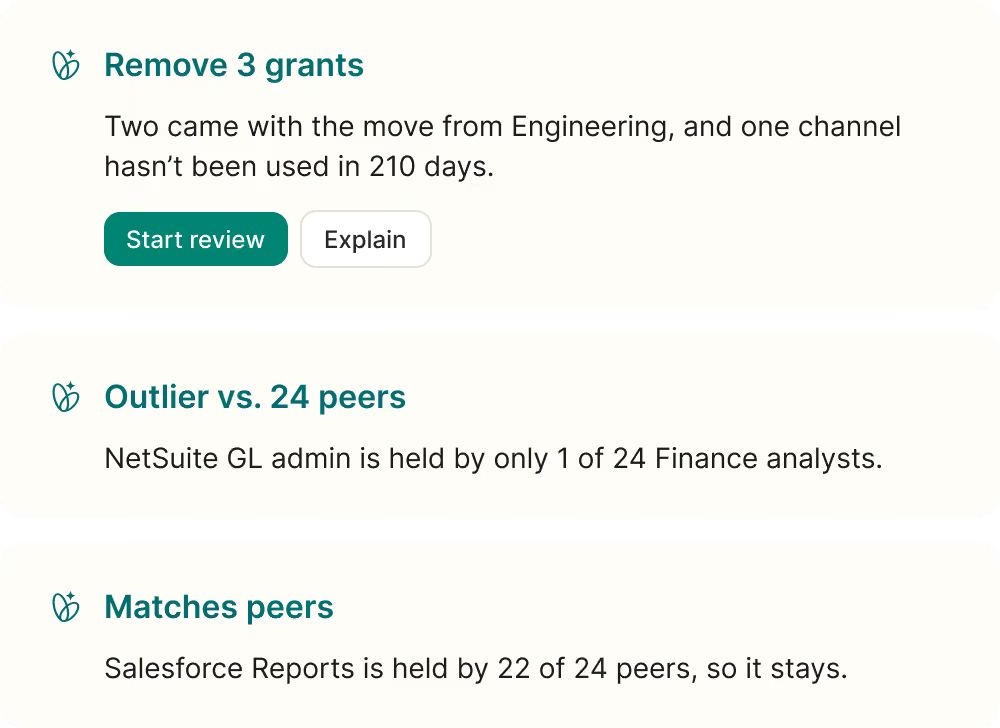
Compared with peers
See how each person’s access compares with people in similar roles.

Drift and outliers
Catch access that no longer fits how the organization works.

Dormant and orphaned access
Find dormant memberships and the orphaned permissions people leave behind.

Trusted remediation

Access reviews that finish
Run user and group reviews with recommendations, one-click decisions, and a full audit trail.

Just-in-time access
Grant access for the task, and remove it when the task is done.

Instant revocation
Remove access on departure day, with nothing left behind.
Works across every IdP, cloud, and agent platform.
Vendor-independent governance for Okta, Entra ID, Workday, AWS, and more, plus the AI agent platforms your teams already use.
Admin roles, API tokens and app assignments across the IdP that governs everything downstream.
Read the blog →Users, role hierarchies, grants and query history, without reading your table data.
Read the blog →Privileged roles, service principals and app registrations, certified against real usage.
Read the blog →Outside collaborators, personal access tokens and Actions workflows, with risky credentials flagged.
Read the blog →IAM bindings, service account keys and Cloud Audit Logs across your resource hierarchy.
Read the blog →Identity findings sent straight to tickets, with every fix verified before the finding closes.
Read the blog →Workspace and Unity Catalog permissions, tokens and audit activity across clouds.
Read the blog →Login roles, inheritance chains, SUPERUSER grants and pgaudit activity.
Read the blog →
Short description of what Oleria reads from this tool.
View integration →IAM permissions, cross-account trusts and CloudTrail activity in one identity graph.
Read the blog →Site hierarchies, file permissions and sharing links that outlive their purpose.
Read the blog →Short description of what Oleria reads from this tool.
View integration →Profiles, permission sets and connected app NHIs resolved into effective access.
Read the blog →Real customers. Real results.
Security teams use Oleria to clean up excess access, get through audits faster, and bring AI agents under control

Oleria is one of those things that once you see it and get it, it’s hard to imagine doing what you’ve been doing without it.
Being able to assess the current state and optimize around least privilege provides the ROI in itself. And the ability to understand what my engineers need will help us provide least-privilege access.
Oleria gives us unparalleled visibility into identity access and usage, saving time and strengthening our compliance posture.
Security & compliance
Enterprise-grade compliance and trust
Oleria meets rigorous standards including SOC 2, ISO 27001, HIPAA, GDPR, PCI DSS 4.0, and NIST/FICAM. Your data stays secure and private: third-party AI providers never learn from your information.
SOC 2 Type II
Independently audited for security, availability, and confidentiality.
ISO/IEC 27001
Certified information security management.
GDPR compliant
Personal data stays personal, with granular permissions.
HIPAA compliant
Protected health information stays protected.
PCI DSS 4.0
Cardholder data handled to the latest standard.