Human Identity Governance
Human identity governance, built on real usage
Right-size access for every employee, contractor, and partner, from day one to departure, based on real usage and peer context.
Access reviews have become rubber stamps
Heading
Access only grows
Every project and role change adds access. Little of it is ever removed.
Reviews without context
Reviewers see a list of entitlements, not whether anyone uses them.
Roles go stale
Role definitions drift out of date months after they’re built.
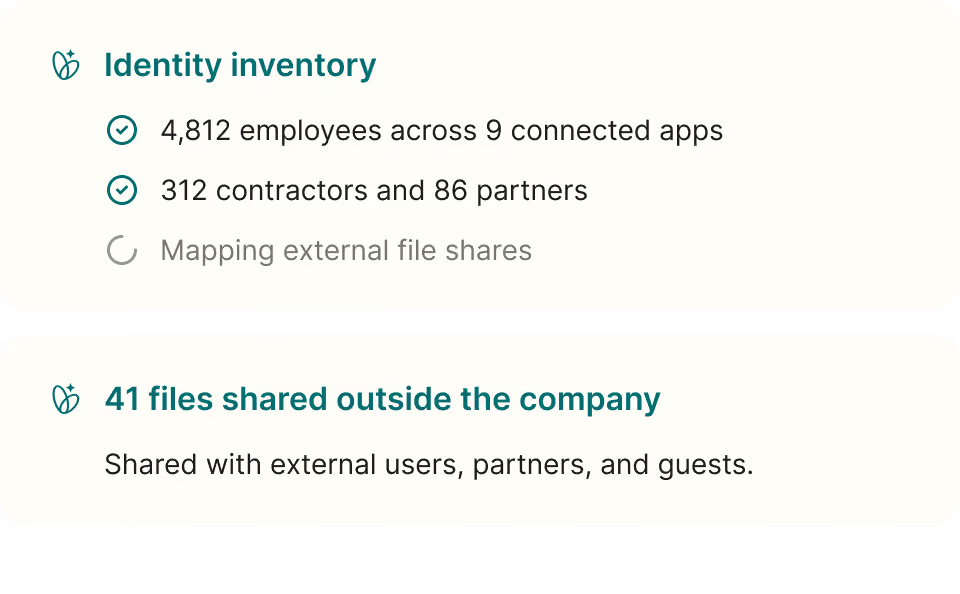
Every employee, contractor, and partner in one view

Every account, group, and permission
See every account, group, and permission across your connected IdPs and SaaS apps.

Files shared outside the company
Including files shared with external users, partners, and guests.
End rubber-stamped access reviews

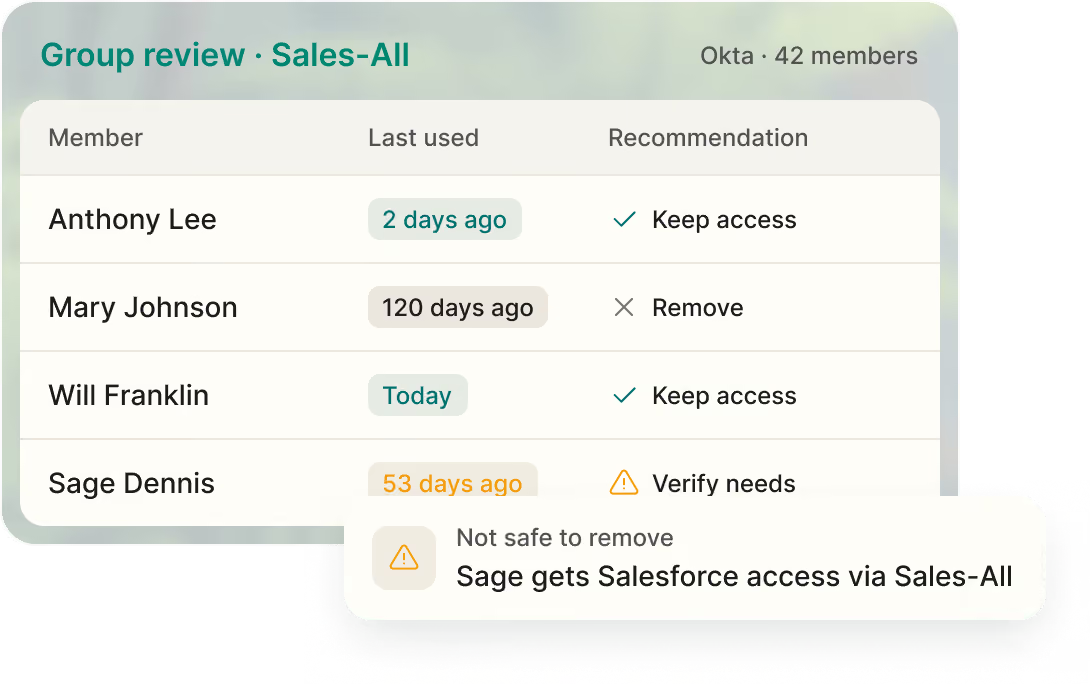
Context on every line
Every line shows usage, dormancy, and peer comparison with a clear recommendation.

Safe removal
When access is rejected, Oleria flags anything that can’t be removed safely.
Automate every joiner, mover, and leaver
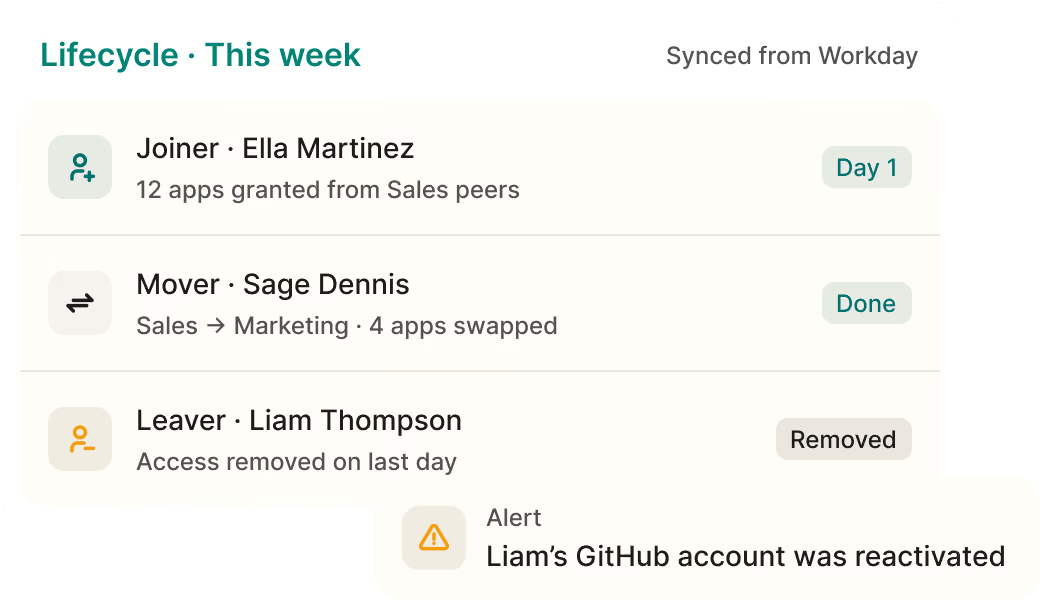
Joiners
New hires get the access their peers have on day one.

Movers
Movers swap old access for new.

Leavers
Leavers lose access on their last day, with alerts if an account is reactivated.
Self-service access that expires on time

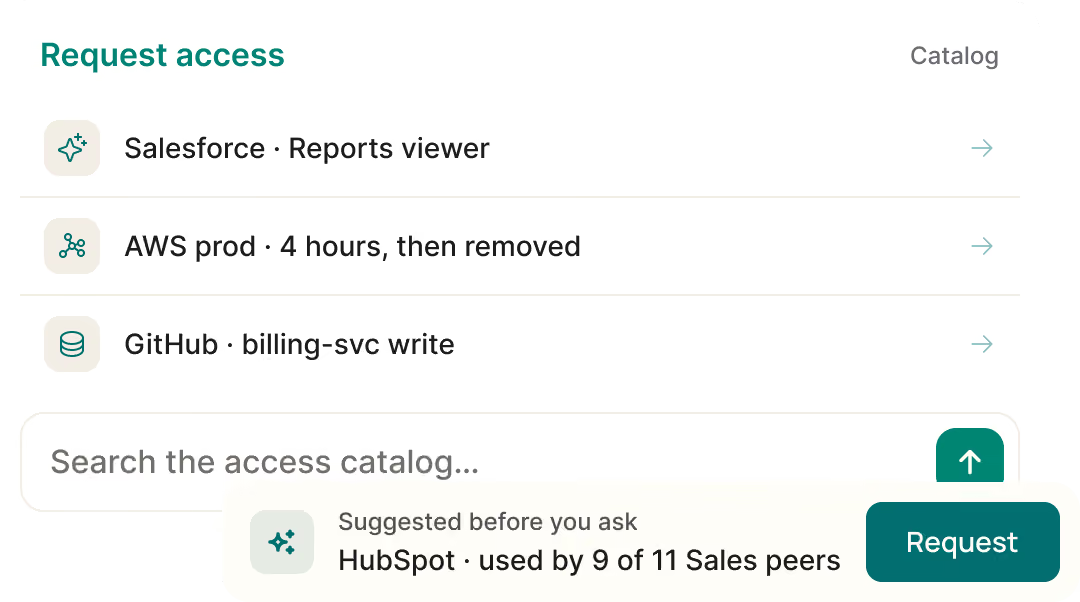
Self-service catalog
Employees request apps, groups, and roles from one catalog.

Approve where you work
Approvers decide in Slack, Teams, or email.

Access that expires on time
Oleria provisions access, then removes it when time is up.
Real customers. Real results.
Security teams use Oleria to clean up excess access, get through audits faster, and bring AI agents under control

Oleria is one of those things that once you see it and get it, it’s hard to imagine doing what you’ve been doing without it.
Being able to assess the current state and optimize around least privilege provides the ROI in itself.And the ability to understand what my engineers need will help us provide least- privilege access
Oleria gives us unparalleled visibility into identity access and usage, saving time and strengthening our compliance posture.
How is Oleria different from legacy IGA?


Questions about human identity governance
What is human identity governance (IGA)?
Human identity governance and administration (IGA) controls who can access what across your organization, from onboarding to offboarding, and proves it to auditors. Oleria does it with real usage and peer context, so access matches what each employee, contractor, and partner needs.
How is Oleria different from legacy IGA?
Legacy IGA relies on static roles and manual reviews. Oleria bases every decision on real usage and peer comparison, and deploys without a consulting engagement.
Does Oleria replace Okta or Entra ID?
No. Oleria AI is the intelligence built into the Trustfusion platform you already know. The naming gives a clear identity to a capability that spans every workflow on the platform, governance, risk, investigations, access, and the MCP endpoint rather than presenting AI as a separate SKU or a bolt-on feature.
No. Oleria is a governance layer on top of your existing identity providers. It connects to Okta, Entra ID, PingOne, and others, and governs access across the apps they manage.
How fast can we deploy Oleria?
The MCP (Model Context Protocol) endpoint exposes Oleria AI's reasoning and graph to any MCP-compatible client — Claude, ChatGPT, your internal copilots, or custom agents. Teams can query Oleria in natural language ("show me everyone with prod AWS access who hasn't logged in for 30 days"), pull context into agentic SOC and IAM workflows, and use the result inside the tools they already trust. The endpoint is read-only by design: agents reason.
Most teams connect their first systems and see insights within a day. Broad coverage follows in weeks, not quarters.
Can Oleria also govern non-human identities and AI agents?
Access reviews and provisioning, external access oversight, risk monitoring, incident investigations, unused and unintended access detection, and authentication posture monitoring. The same unified graph and Oleria AI reasoning underpin every one of them — which is what makes Trustfusion feel like one platform rather than a suite of point tools.
Yes. Oleria governs human identities, NHIs, and AI agents in one platform, from the same usage and access data. See the Non-Human Identities and AI Agents pages for how each is governed.
What is the difference between IAM and IGA?
Access reviews and provisioning, external access oversight, risk monitoring, incident investigations, unused and unintended access detection, and authentication posture monitoring. The same unified graph and Oleria AI reasoning underpin every one of them — which is what makes Trustfusion feel like one platform rather than a suite of point tools.
IAM (identity and access management) controls how people sign in and what they can reach. IGA governs that access over time: who should have it, who approved it, whether it is still used, and how you prove it to auditors. Oleria adds IGA on top of your IAM stack.